Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

CrowdStrike Extends Endpoint Security to Stop Software Supply Chain Attacks

Software supply chain attacks pose a critical enterprise threat. In the first half of 2026, these attacks increasingly used malicious software packages uploaded to public software registries, the CrowdStrike 2026 Threat Hunting Report found. Adversaries are poisoning open-source packages and exploiting the same dependencies that AI-assisted development tools and agentic applications pull onto enterprise endpoints every day.

Peer Pressure: Inside the Sality Botnet Disruption Operation

On August 31, 2026, CrowdStrike's Counter Adversary Operations team, in collaboration with international law enforcement and industry partners, executed a coordinated disruption of the Sality peer-to-peer (P2P) botnet, a criminal infrastructure that has operated with seeming impunity for more than two decades. The botnet enabled the operator to distribute malicious payloads to over 15,000 infected machines worldwide.

CrowdStrike Falcon Guardian Defines the Next Generation of AI Security

AI has rapidly evolved into a technology that takes action. AI agents can reason, access enterprise systems, and execute tasks autonomously at machine speed, often with the full permissions of the users they serve. As these agents proliferate across the enterprise, organizations need to understand where they operate, what they do, what they can access, and how to stop threats before they become breaches. This shift demands a new approach to AI security.

The Threat Intel Workflow is Broken

A critical alert shouldn’t come with a scavenger hunt. But answering the obvious questions can still send analysts bouncing between threat reports, adversary profiles, underground activity, vulnerability data, and hunting tools. See how CrowdStrike’s Threat Intelligence Agent, powered by Charlotte AI, brings those answers together and helps turn them into action, from hunting queries and dark web monitoring to vulnerability checks and automated workflows. The analyst stays in control. The busywork doesn’t.

Intelligent Telemetry Control and Federated Search with Falcon Next-Gen SIEM

See how CrowdStrike combines intelligent telemetry control with Falcon Next-Gen SIEM Federated Search to optimize data costs without sacrificing investigative depth. Learn how Falcon Onum filters, enriches, masks, and routes telemetry in motion before ingestion.

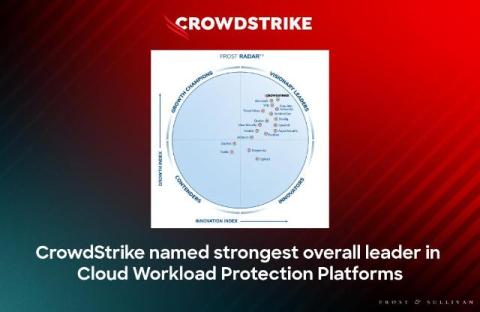
CrowdStrike Named Strongest Overall Leader in 2026 Frost Radar: Cloud Workload Protection Platforms

We are proud to announce that Frost & Sullivan has named CrowdStrike as the strongest overall leader in the Frost Radar: Cloud Workload Protection Platforms, 2026. CrowdStrike earned the highest scores in Innovation and Growth among 18 companies benchmarked from a field of more than 45 qualified participants. Today’s cloud attacks are designed to hide in plain sight.

How CrowdStrike Delivers Falcon Privileged Access

Breaches don’t always start with malware. Increasingly, adversaries simply log in with valid credentials and when those credentials come with standing privileges, attackers inherit that access instantly. In this Lightboard Lab, learn how CrowdStrike is rethinking traditional privileged access with Modern Privileged Access. See how continuous evaluation of identity, device trust, security risk and business context can eliminate standing privileges and help ensure the right person gets the right access, in the right context, right when they need it.

Benchmaxxing: When the Benchmark Becomes the Target

Public benchmarks in AI provide important signals and allow for regression testing, directional validation of model updates, and public discussion of capabilities and limitations. But the more attention a benchmark receives, the stronger the incentive to optimize for it. Once a score becomes the goal, teams start benchmaxxing: optimizing for the benchmark rather than the capability it is meant to measure. This is a familiar problem in the AI space.

Falcon Exposure Management Custom Sensor Scanning: Demo Drill Down

In this Demo Drill Down, learn how Manual Sensor Scan enables teams to create targeted Python-based checks for pre-CVE vulnerabilities, supply chain risks, proprietary software, and other environment-specific conditions. See how built-in helper functions simplify custom detection logic and how identified findings are brought directly into Falcon Exposure Management for investigation, prioritization, and remediation.