Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

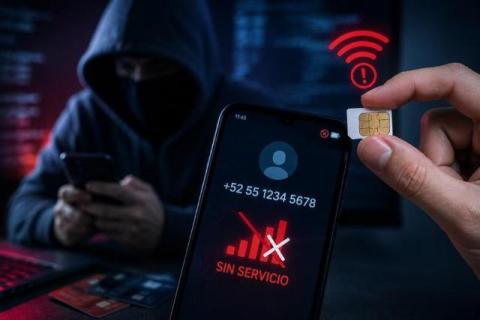
Phone Numbers as an Attack Surface: What SIM Swap and Data Leaks Actually Expose

The majority of security teams' work time is devoted to passive mitigation, password rotation, enabling multifactor authentication, or making authentication more complex and giving much more attention to the phone number in recovery than to other factors. Not a communication channel, but rather an identifier, as said, it's used in many aspects of tools, banking, and also e-mail, and when all thieves discover the methods of using it, that's when trouble arrives.
SalatStealer Malware: Inside a Credential Stealer Built for Repeat Use

SalatStealer is a Go-based infostealer family first observed in August 2026, built for x86 Windows environments and focused on credential theft. Its documented capabilities include stealing authentication credentials, hiding executing code, and degrading security software.

Managed identity threat detection and response (ITDR): what MSPs and security teams need

For MSP service owners and technicians, managed identity threat detection and response comes down to a practical service question: who investigates a compromised client account, and who can contain it after hours? Consistent handling across client environments depends on clear ownership from prevention through recovery. Start by checking the identity coverage already included in your managed detection and response (MDR) service or extended detection and response (XDR) deployment.

What Is Identity Governance and Administration (IGA)? A Complete Guide

Disconnected identity systems create the access risk, audit friction, and IT overhead that identity governance and administration (IGA) is built to close. The 2026 Verizon Data Breach Investigations Report found credential abuse in 39% of breaches. IGA combines policy, certification, and compliance evidence with automated provisioning, deprovisioning, and access requests to keep access aligned with business needs and reduce that risk.

AI security solutions: what they are and how to choose one

Employees can start using an AI tool and share business information with it before IT has reviewed the service or the data involved. AI security solutions help businesses bring that exposure under control without treating every useful AI interaction as something to ban. This guide is written for SMB IT decision-makers evaluating protection for employees who use public or business generative AI tools, often with support from a managed service provider (MSP).

How to reduce DLP false positives

DLP false positives bury real incidents under benign alerts and push teams to switch off the controls they bought. Most of that noise is configuration. Classify sensitive data before enforcement, pair content matches with identity and destination context, phase policies from simulation to blocking, and read override reasons as a tuning signal. Track the trend per policy, and you can show an auditor what the controls do.

What Is Agentic AI Security? The 3 Layers and Their Owners

Two of the three layers of agentic AI security already have an owner in your organization, and the third has none. Identity falls to IAM and interaction falls to AppSec, because the controls at both layers extend products those teams already run. The behaviour layer covers what the agent does on the infrastructure once it is running, and it sits between a platform team with no security mandate and a SOC with no sense of what normal looks like for an agent. That gap is where a coerced agent works.