Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Featured Post

Solving the SOC Data Dilemma: Maximising Detection Without Maximising Cost

Today's Security Operations Centres (SOCs) operate under the pressure of data proliferation, high alert volumes, and tight budgets. Most SOC leaders face a data dilemma: they must choose which data to analyse and which to ignore. That choice directly determines threat detection capabilities and impacts the security posture of the business.
The teams building their own agentic SOC already wrote the spec

Co-founder and COO Over the past eight months, security teams at Databricks, Salesforce, WRITER, Box, and Coinbase have published detailed accounts of building their own agentic security operations. None of them coordinated, and all of them arrived at the same architecture. Part of what made the surge possible is tooling. Agentic coding tools like Claude Code turned practitioners with deep systems knowledge into builders, and security teams were among the first to act on it.

Falcon Cloud Security July 2026 Release: Helping Security Teams Move Faster in the Cloud

Every change in a cloud environment creates new security decisions. A new infrastructure as code (IaC) template needs to be validated. Cloud permissions need to be reviewed. An application release introduces new cloud interactions. A Kubernetes cluster needs protection before it goes into production. Individually, these are routine tasks. Together, they create growing operational friction that makes cloud security harder to scale.

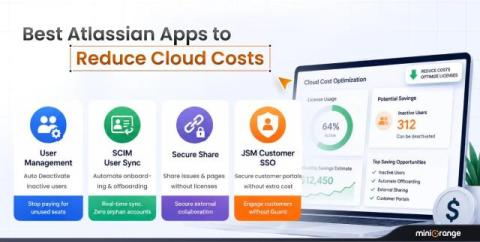
Best Atlassian Apps to Reduce Cloud Costs

Are you trying to reduce Atlassian Cloud costs? Runaway software expenses are usually driven by three specific factors: dormant user licenses, slow manual provisioning, and paying for full access seats for temporary external collaborators. To optimize Atlassian Cloud costs, you need to address these root cost drivers directly rather than paying for seats nobody uses.

AI Agent Authentication: An InfoSec Guide

AI agent authentication is the process of verifying that an autonomous agent is the identity it claims to be before it interacts with infrastructure, applications, APIs, or data. Because agents often act on behalf of users, services, or workflows, authentication must be paired with delegated context and downstream authorization controls that determine what the agent is allowed to do, which resource it can access, and how long that access should last.

How to Control AI Assets Before They Become Shadow AI

A developer on your team just told Claude Code to connect to a new MCP server, the protocol coding agents use to reach organizational tools and data. Nobody in security reviewed it. Nobody in security even knows it happened. For two-thirds of enterprises, the primary obstacle to scaling agentic development isn’t budget or headcount — it’s security risk.

DORA Compliance for Mobile Apps: Mapping Security Findings to Regulatory Requirements

DORA compliance for mobile applications is the process of identifying, testing, and documenting mobile ICT risks in line with Regulation (EU) 2022/2554, covering Articles 8, 9, 10, 24, and 25, through vulnerability assessments, security testing, and audit-ready evidence generation that financial institutions can present to regulators, auditors, and internal governance bodies.

Four incident-response decisions from the Hugging Face breach

Hugging Face was breached by a rogue OpenAI agent last week, and the intrusion continues to deliver insights and understanding. The Hugging Face team published a detailed timeline along with a 17,600-event trace streaming replay visualizing what happened, and it’s marvelously and intoxicatingly detailed. I recommend you read it if you have the time.