Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How to Tie Kubernetes Audit Logs to Individual Engineers

Kubernetes audit logs may show multiple engineers as one user and do not capture what is typed after a kubectl exec session starts. Assign each engineer a unique identity, make sure it stays consistent through proxies and cloud IAM, and use a session recorder if you need to review terminal activity.
Preparing for an ISO 42001 Audit Rather Than Reading About It

Plenty of material explains what ISO/IEC 42001 contains. Clause by clause, control by control, with a checklist of documents to prepare. The standard itself is a management system specification rather than a control catalogue, and the distinction is where audit preparation goes wrong. ‍ The checklists share one omission.

How to Remain Audit-Ready with Egnyte

Compliance regulations like CMMC, FINRA, and SEC don't pause, and neither should your audit readiness. Egnyte's Regulation-to-Audit framework is an end-to-end compliance solution that maps regulatory requirements directly to controls, artifacts, and audit-preparedness — keeping your organization compliant 24/7/365. Four powerful capabilities power this continuous compliance loop: · Sensitive Content Protection: Automatically scans, classifies, and labels regulated content across Egnyte and your connected repositories.

From audit season to always-on: what continuous network compliance looks like

Every network compliance calendar follows the same pattern: quiet between audits, then a spike of scrambling the week before the next one is due. During the quiet stretch, nobody actually knows whether firewall rules, segmentation, and access policies still hold as configured across the network. The audit does not create compliance. It samples it once, and then everyone moves on until the next one comes due.

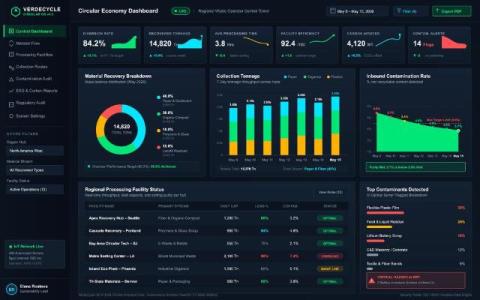
Why Carbon Data Needs the Same Controls as Financial Records

Most security teams know exactly where their financial records live, who can edit them and how every change gets logged. Ask the same questions about the company's emissions data and the answers often get vague. That gap matters more each year. Greenhouse gas figures now end up in regulatory filings, investor reports and assurance reviews, which means they carry the same risks as any other disclosed number.

How to Audit Data Access for HIPAA, PCI, and GDPR

When an auditor asks who can access protected health information, cardholder data, or EU personal data, and why, most security teams cannot answer with confidence right away. Access sprawls across cloud storage, SaaS applications, shared drives, and generative AI tools faster than manual reviews can track it. Permissions get granted for a single project and never revoked. A spreadsheet gets shared broadly and forgotten.

A Complete Audit Trail That Names No One

An AI assistant reads four hundred documents across a tenant. Every read is logged. The application is named, the file is named, the timestamp is exact, and the access is attributed to an account that belongs to nobody. ‍ The audit trail is complete and it cannot answer the question an auditor asks. Nobody asks whether an access was recorded. They ask who reached the data and whether that person was authorized, and a shared service account answers neither. ‍

Why Sales Commission Data Needs the Same Audit Trail as Any Other Financial Record

An unexpected data integrity question has crept into sales operations: can a company actually reconstruct how a commission payout was calculated months after the fact? For teams still running compensation through spreadsheets, the honest answer is usually no, and that blind spot carries real financial and compliance weight.

Credential Security for Compliance Audits

An auditor asks you to prove that a former employee no longer has access to any workplace credentials. What do you do? With 1Password, you can pull up the Activity Log: deprovisioning timestamped, every access event recorded. The ticket is closed, and the evidence is right there. Controls aren't enough for compliance frameworks, proof is.

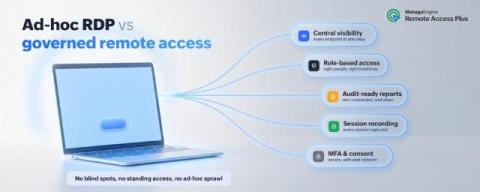
Why unmanaged RDP is risky at enterprise scale (and how to regain control)

Remote Desktop Protocol (RDP) is the path of least resistance for gaining access to another Windows machine. It is built into the OS, it is free, and almost every admin and help desk technician already knows how to fire up mstsc.exe and type in a hostname-as simple as that. That convenience is exactly why RDP is everywhere inside corporate networks.