Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

SMBs Hit a Cybersecurity Breaking Point as 91% Fear AI-Driven Attacks, Driving Shift to MSP-Led Security Models, WatchGuard Finds

LONDON, May 20 2026 -New research from WatchGuard Technologies, a global leader in unified cybersecurity for MSPs, reveals that while most businesses believe they are adequately staffed, the complexity, speed, and scale of modern threats - especially those powered by artificial intelligence - have outpaced what internal teams can realistically manage. The result is a fundamental shift away from do-it-yourself security toward externally delivered, always-on protection models.

Balancing AI Innovation and Risk: Enhance Organizational Resilience

‍ Artificial intelligence (AI) offers businesses vast opportunities to boost efficiency, improve decision-making, and innovate faster. Yet, these benefits come with significant risks that can impact business operations and resilience if not managed carefully. This article explores how organizations can balance leveraging AI’s advantages while controlling its inherent risks. ‍

Codex builds at AI Speed, 1Password Secures it

Secure secrets for agentic workflows with 1Password MCP Server and Codex As AI agents write, execute, and ship production code, they need access to systems like databases, APIs, and deployment pipelines. With 1Password Environments MCP Server for Codex, instead of putting credentials directly into prompts or files, we provision a secure runtime environment where secrets are mounted, used, and discarded, with user authentication required at the moment of access.

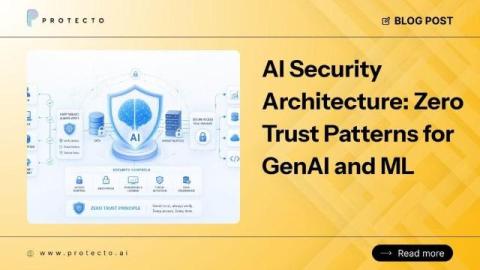
AI Security Architecture: Zero Trust Patterns for GenAI and ML

There is no doubt that AI, or Artificial Intelligence, is rapidly changing how businesses are operating. However, it also brings new risks when it comes to data. As per industry reports, 72% of companies mention that there has been a significant increase in organizational cyber risks. It is therefore necessary to have a strong AI security architecture that helps to protect sensitive information. In light of this, 85% of organizations are now increasing their cybersecurity budget.

Guarding the Manufacturer's Core: Securing Intellectual Property in the Age of AI at Renesas

Organizations like Renesas face critical risks when utilizing AI, as these platforms often incorporate user-submitted data into their models. Significant security incidents have occurred where sensitive source code, firmware, and proprietary designs were inadvertently made public after being uploaded for testing. A major business risk involves the potential loss of intellectual property, which can directly impact an organization's primary revenue streams. Beyond data leakage, AI presents risks through "poisoning" and the fact that AI-generated output is frequently inaccurate.

Building the Post-Mythos Security Organization: From Episodic Security to Continuous Assurance

In an era where AI accelerates both innovation and adversarial capability, security leaders are confronting a difficult reality: traditional approaches to cyber defense are no longer sufficient. Cyberhaven’s Office of the CISO is responding with a forward-looking strategy designed not simply to keep pace with emerging threats, but to fundamentally redefine enterprise readiness in a post-Mythos world.

Misconfigured Security Controls Open the Door for Storm-2949

The Microsoft Defender Security Research Team and Microsoft Threat Intelligence documented a campaign in which Storm-2949 abused Microsoft Entra ID accounts to exfiltrate data from Microsoft 365 and Azure environments. The attack shows how cloud intrusions increasingly unfold through identity systems, administrative features, and legitimate platform capabilities rather than obvious malware or traditional endpoint compromise.

How AI Is Transforming Detection Engineering

One of the most important shifts AI enables in detection engineering is changing where engineers spend their time. Traditionally, a significant portion of detection development effort is consumed by implementation details: writing complex SQL queries, building enrichment pipelines, handling edge cases, tuning rule logic, writing tests, documenting detections, and repeatedly iterating on detection logic. Those tasks are necessary, but they are also time-consuming.

Shadow MCP Servers: The AI Infrastructure You Can't See

In 2012, the "Shadow IT" crisis was employees putting files in Dropbox for convenience. In 2026, the crisis is Shadow MCP. Instead of a simple file storage app, security teams are now facing unvetted AI agents with the power to read from and write to internal systems. These servers are often running on infrastructure that was never reviewed, never approved, and remains entirely invisible to governance.

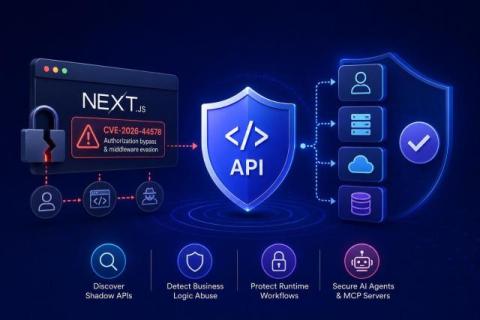
Next.js Vulnerability Exposes Credentials and Protected Data - Why Runtime API Security Matters

A newly disclosed security issue, tracked as CVE-2026-44578, affecting Next.js applications is raising concerns across the developer and security communities after researchers identified multiple authorization bypass and middleware evasion paths that could expose protected application data and credentials. The vulnerabilities impact several versions of Next.js and allow attackers to bypass middleware-based authorization controls using crafted requests and route manipulation techniques.