Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Is a SOC 2 Report Enough to Assess a Cloud Vendor?

A vendor sends over a SOC 2 report. It lands in the queue, someone reads the cover page, sees the auditor's name and a clean-looking opinion letter, and marks the assessment complete. The reviewer moves on to the next vendor. Multiply that by a few hundred vendors a year, and it becomes less of a decision and more of a reflex.

Report: One-Quarter of Breaches Are Enabled by AI-Driven Attacks

A new report commissioned by IBM has found that one in four breaches is now AI-enabled, up 56% from last year. “Most AI-driven attacks reported in the study targeted critical infrastructure sectors (62%), with financial services and energy organizations experiencing the highest concentration, raising the risk of broader systemic disruption,” the report says. “Financial services breaches were reported to cost on average $6.3 million, while energy breaches cost on average $5.2 million.

The Rise of the 'Non-Human Insider': When AI Agents Become the Threat

For years, cybersecurity has had a familiar villain: the external attacker. The hacker breaking through the firewall, stealing credentials or exploiting an unpatched vulnerability. It is the scenario we have trained for, built defenses around and spent decades trying to prevent. But the next major breach may not begin with someone breaking into your environment at all, it may begin with an AI agent that already has access.

What is Security Posture Management and Why is it Important?

Modern organizations don't operate from a single server room anymore. Today's enterprise environment spans dozens of cloud services, SaaS applications, APIs, AI agents, and non-human identities, all of which are continuously changing. A quarterly security audit is no longer a safety net, but now considered a gap.

451 Research report: How agentic AI is redefining identity security

In the short time that AI agents have been a part of the enterprise, they have upended many of our bedrock assumptions about the nature of identity, access, development, and work itself. At 1Password, we’ve been in the trenches of the agentic revolution; we’ve seen its positive impact on productivity, and the serious concerns it raises about security.

Secure AI Written Code Before It Ships: Salt Code

AI coding assistants are transforming how enterprise software gets built. Developers at every level are prompting their way to production-ready APIs, MCP integrations, and agentic workflows faster than any security team can review them. The problem is that none of those assistants knows your internal security standards, regulatory obligations, or risk tolerance. The result is insecure patterns shipping unnoticed, vulnerabilities discovered downstream when fixes are costly, and compliance becoming a guessing game on every commit.

Why Annual Mobile App Security Testing Is Not Enough on Its Own

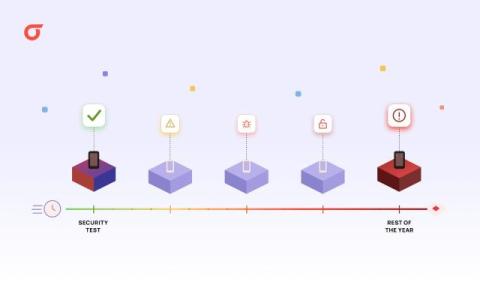
Annual testing secures a moment. Your app keeps changing. Here is how to cover the interval between assessments. An annual penetration test answers a precise question. Was this version of this application secure when a skilled tester examined it? That answer has real value. It is independent, deep, and finds business logic flaws that no scanner will ever surface. It is also a photograph.

How NER Finds Sensitive Data Hidden in Documents #shorts

Sensitive data detection was much easier when information lived inside structured databases. Tables, columns, field names, and predictable data types gave security teams a clear map of where sensitive information lived. But when sensitive data moved into documents and PDFs, that map disappeared. Names, addresses, phone numbers, credit card numbers, and other sensitive information could be buried inside natural language.