Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How autonomous pentesting kills false positives

Ask any security engineer what they actually think about their vulnerability scanner, and you will get a version of the same answer. They trust maybe 20% of what shows up in the patching queue. The rest gets a suspicious glance, and a slow death in a backlog. That is the real cost of a false positive. It is quiet, it compounds, and it hollows the tool out from the inside. It is also the reason autonomous pentesting came to replace hypotheses with confirmed exploits.
How SLED can win the cybersecurity race with agentic AI

Adversaries are using AI to launch cyber attacks in record time, forcing security teams to measure responses in minutes instead of months. Phishing campaigns built with large language models (LLMs) achieve click-through rates 4.5 times higher than traditional methods,1 and the average time between initial compromise and lateral movement has fallen to just 29 minutes.2 This is a 65% increase from the prior year.2 State and local governments and higher education institutions are at an inflection point.

Why Business Leaders Need a New Response Model to AI-Enabled Incidents

Originally published by Cybersecurity Insider. Over the past decade, cybersecurity threats have evolved from a technical issue into a key driver of business and operational risk. Artificial intelligence is accelerating that shift even further, changing the game once again. In 2026, AI in cybersecurity is multifaceted: a tool for defense and incident response, but also a powerful accelerator for attackers. AI-enabled incidents rarely stay contained within the security function.

Decommissioning AI Agents: What to Look For in the Tooling

Gartner predicted in mid-2025 that more than forty percent of agentic AI projects would be canceled by the end of 2027, citing escalating costs, unclear business value and inadequate risk controls. Treat the figure as a forward-looking estimate rather than a measurement, since canceled projects tend to be quietly renamed, absorbed or left to lapse rather than formally closed. ‍

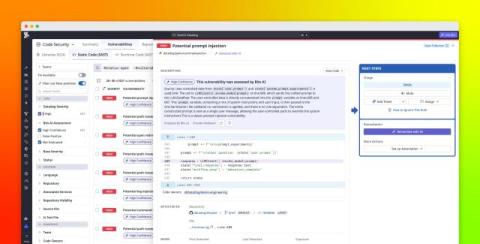
Detect vulnerabilities in LLM applications with Datadog's AI-native SAST

AI coding tools help developers build and deploy LLM applications quickly, but this speed comes with new security risks. Traditional static application security testing (SAST) tools that are pattern based weren’t designed to detect LLM-specific issues such as prompt injection sinks and exposed system prompts. These vulnerabilities often don’t become apparent until applications are already running in production, when remediation is more difficult and expensive.

From signals to systemic risk: Building Risk AI

Security and engineering teams contend with a constant stream of signals about vulnerabilities, incidents, misconfigurations, identity risks, control gaps, and other findings across their environments. But an individual finding’s severity does not always reflect its potential organizational impact.

Agentic First Security -- Customer Brown Bag - August 20th, 2026

Join Jeremy Powell, CISO of Sumo Logic, to learn how AI-powered agents are reshaping modern security operations. Discover the key principles, governance, and best practices for building an agentic security program that enhances analyst productivity, accelerates threat response, and strengthens organizational resilience.

Give your agents capabilities

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

From all-or-nothing to task-based OAuth consent

Since June, developers have created thousands of third-party OAuth apps on Cloudflare, with more than a million authorizations since. OAuth makes delegated access possible. It lets applications act on a user’s behalf without asking them to handle long-lived credentials or hand over a password. That model works well when an application can describe its access needs with a small set of scopes. Developers use OAuth for SaaS integrations, internal tools, CLIs, and agents.