Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

OWASP LLM Top 10 2026: the model will be fooled, the question is what breaks

The OWASP GenAI Security Project published the 2026 edition of its Top 10 for LLM Applications. Prompt Injection stayed at number one. Sensitive Information Disclosure stayed at number two. Read the headlines and you would conclude that not much moved. Something did move, and it is not in the rankings. The project leads open by telling you to stop trying to build a model that cannot be fooled, and to build the system around it so that when the model is fooled, nothing important breaks.

What an AI Compliance Audit Involves, Stage by Stage

An AI compliance audit is less mysterious than its absence from most planning suggests. Someone outside the organization reads what you wrote down, then samples real systems to test whether the organization does what the documents describe. The distance between those two things is where findings come from. ‍ Three different exercises get called an AI audit, and they run differently. Certification against a management standard follows a defined two-stage process.

How Cato AI Security Keeps Up With Claude

Claude is moving quickly. Cato is innovating alongside it. With inference hooks, skills posture, and seamless deployment, teams can adopt new AI capabilities with security controls that are ready from day one. Claude’s rapid innovation is reshaping what everyday employees can do with AI. It is no longer just helping people write faster or summarize information; it is becoming a hands-on work companion that can research, reason, build, and take action across business workflows.

The Agentic AI Security Adoption Matrix: Autonomy Scales Where Control Exists

Agentic AI is crossing a threshold. It is no longer just generating content or answering questions. It is beginning to plan, decide, and execute actions across tools, systems, and workflows. That shift unlocks real efficiency, but it also changes the security equation. When an AI system can act, it becomes part of your operational attack surface. It can be influenced, misdirected, or exploited. It can make mistakes at machine speed. And if it has permissions, it can create real impact.

8 Best Encrypted Email Services to Protect Yourself With In 2026

Most successful hacks and data breaches are perpetrated through email. In a perfect world, everyone would find safer methods for communication, but since email isn't going anywhere anytime soon, encrypted email is our best option. Since Internxt doesn't have its own encrypted email yet, we've assembled a list of the best encrypted email services you should use in the meantime.

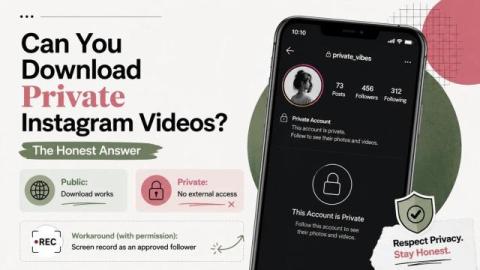
Can You Download Private Instagram Videos? The Honest Answer

Search for 'private Instagram downloader' and you'll find dozens of sites claiming to do it. Most of them can't - and the ones that claim otherwise are usually either misleading or asking for something you shouldn't give them (like your Instagram password). The honest answer depends on which specific situation you're in. Here's the full picture, without the misleading promises - and where a free instagram downloader actually works.

AI Agents & Cybersecurity: Why AI Agents Are New Trust Boundaries | A10 Networks

AI Agents & Cybersecurity: Why AI Agents Are New Trust Boundaries AI agents are more than just another virtual machine—they are autonomous entities delegated with power, introducing entirely new trust boundaries into modern network architectures. In this discussion, A10's Arjoyita Roy and Jamison Utter discuss why traditional security controls fall short when managing AI agents and why cybersecurity professionals must design new security perimeters and controls around these evolving AI workloads.

Automate Inactive User Suspension with JumpCloud Workflows

Say goodbye to manual offboarding checks and dormant account risks! Join Derek Johnson as he demonstrates how to leverage JumpCloud’s user inactivity rules and Directory Insights (DI) trigger events to instantly automate account suspensions, group isolations, and admin notifications. We walk through configuring inactivity thresholds, mapping JSON parameters, and executing a live test run so you can streamline your IT operations today.

Avoid Azure secret rotation with secretless authentication

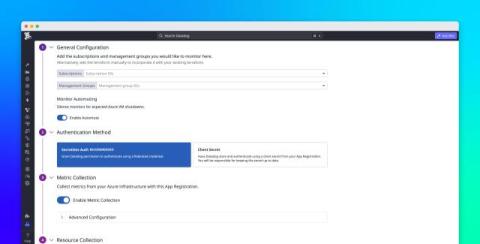
Many observability platforms authenticate to Microsoft Azure by using client secrets. Teams must create, store, and periodically rotate these secrets to keep receiving the telemetry data that they need. This recurring maintenance adds operational overhead and increases the risk of ingestion outages that occur when secrets expire.