Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

5 Reasons Your DAST and SAST Scans Miss BOLA & BFLA

Every API security evaluation reaches the same objection: “We already run SAST and DAST.” The objection is fair. Static Application Security Testing (SAST) reads source code before release. Dynamic Application Security Testing (DAST) probes a running application from the outside. Both belong in continuous integration and continuous delivery (CI/CD) pipelines. Both also struggle with the two Application Programming Interface (API) flaws that matter most.
Scanning AI Assets: Catching What SCA and SAST Might Miss

Your standard application security tools are designed to protect your software pipeline by checking third-party components for known vulnerabilities (via SCA), analyzing source code for security flaws (via SAST), and scanning for accidentally exposed credentials (using secret scanners). But if a developer drops a SKILL.md file into their coding agent, installs a plugin from a marketplace, or pulls in an APM manifest, your AppSec scanners may not catch it.

Why Traditional SAST Fails on AI-Generated Code

AI didn't just speed up software development, it changed what application security programs must defend. As AI coding assistants generate code at machine speed and developers integrate AI agents, models, and RAG pipelines into production, traditional scanners generate endless backlogs of unprioritized alerts.

The Best Application Security Testing Tool Isn't a Scanning Tool Anymore

For years, the application security testing tool category was defined by a simple question: can it find vulnerabilities? The better the scanner, the better the tool. That model made sense (for the most part) when humans wrote every line of code and security teams could reasonably review what developers shipped. That model is now obsolete.

SAST False Positives Are Breaking Your Vulnerability Remediation Workflow

SAST scanners do their job well. The problem is their job stops at flagging vulnerable functions, not confirming whether those functions are reachable in your application. The result is a vulnerability remediation workflow full of findings that developers spend sprint cycles investigating, only to conclude they aren’t exploitable. Seemplicity’s Code Analyst closes that gap before the finding ever hits the queue. Security tools are supposed to make developers’ jobs easier.

Best MAST Tools in 2026: Top Mobile Application Security Testing Platforms Compared

Your mobile app ships as a compiled binary to millions of devices you do not control. Anyone can decompile it, extract hardcoded secrets, reverse-engineer the logic, and exploit business-logic flaws that no automated scanner catches. Yet most security programs still treat mobile as an afterthought, running a web-focused SAST tool against mobile source code and calling it done. That approach misses platform-specific risks.

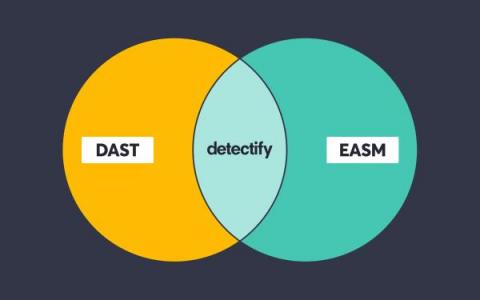
Attack Surface Monitoring vs DAST: Why security teams need both

Attack Surface Monitoring has become a critical component of modern cybersecurity programs. As organizations scale their cloud environments, applications, APIs, and third-party services, so does their external attack surface. Every new cloud instance, API endpoint, marketing microsite, and third-party SaaS tool expands your perimeter. But there are two hard truths for security teams: You cannot protect what you don’t know exists, and you cannot secure what you don’t deeply test.

Appknox vs Code-Centric SAST Tools: What Source Code Analysis Cannot See in a Mobile App

Your source code passed every scan. Every code review approved. Every linter ran clean. Your users just downloaded the compiled binary. Those are not the same artifact. Code-centric SAST tools analyze the code you write. Appknox analyzes what you ship. This is not a feature distinction. It is an architectural one, with direct consequences for what gets caught and what does not.