Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Best Cloud Compliance Tools in 2026: From Audit-Prep to Runtime Verification

What are the three types of cloud compliance tools? Audit-prep platforms (Drata, Vanta) automate evidence collection for certifications. Security posture management/CSPM (Wiz, Prisma Cloud) scan configurations at a point in time. Runtime compliance verification (ARMO, Sysdig) monitors actual workload behavior continuously. Choosing the wrong type means solving for the wrong problem. What is compliance drift and why does it matter? The gap between your last scan and your current state.
Can WAF prevent browser attacks that break PCI compliance?

The answer to whether WAF can see and prevent browser attacks that break PCI compliance depends on the lens you use. Through the lens of Requirement 6.4.2, the answer is mostly yes. But through the lens of 6.4.3 and 11.6.1, it gets a little blurry. Requirement 6.4.2 is about stopping web-based attacks at the application layer by inspecting outbound and inbound HTTP traffic at the server side.

PCI DSS Penetration Testing Requirements Explained

Overall, PCI DSS 4.0.1 is a set of 12 requirements distributed over six goals as a security standard for credit cards and debit cards. Not having proper documentation, poor protocols, or insufficient penetration testing may be among the reasons as to why PCI DSS audits fail.

Healthcare Ransomware Recovery: A HIPAA-Compliant Response Framework

Healthcare remains the most targeted sector for ransomware attacks, with 238 ransomware incidents reported to the FBI in 2024 alone. The Change Healthcare attack demonstrated the cascading impact a single breach can have across the entire healthcare ecosystem, affecting payment processing for providers nationwide and ultimately compromising data on an estimated 190 million individuals.

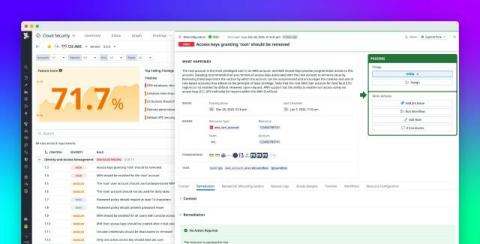
Scale compliance across global frameworks with Datadog Cloud Security

Security organizations are expected to keep pace with a growing set of regulatory and industry requirements as their cloud environments grow. Yet maintaining compliance in modern, fast-moving infrastructure is increasingly difficult. Cloud resources change by the minute, teams adopt new services without centralized oversight, and evidence needed for audits is often scattered across tools and providers.

Introducing Mend.io's AI Security Maturity Survey + Compliance Checklist available today

Today, we’re excited to launch two practical tools to help teams quickly understand their AI maturity, quantify AI risk, and gather the evidence executives will ask for in 2026: an interactive AI Security Maturity Survey (with a personalized score and mapped recommendations) and a companion AI Security Compliance Checklist. Both are aligned to industry standards and built to be immediately useful in discovery, audits, and planning.

How to choose the best access review software: A buyer's guide

As businesses continue to adopt new technologies and expand their digital ecosystem, about 72% of organizations report that overall security risks have never been higher. Access-related vulnerabilities, in particular, have emerged as one of the top cybersecurity concerns, since every new tool or system introduces additional access points, users, and permissions to manage.

Challenges in Meeting Multi-regulatory Compliance

RBI. SEBI. IRDAI. CERT-In. These are just some of the regulatory frameworks a modern enterprise must comply with today. When companies operate under multiple regulators, overlapping mandates often create more confusion than clarity, with different reporting timelines, expectations, and audit pressures.