Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Report: AI Chatbots Are More Effective at Building Trust Than Human Scammers

A study has found that AI chatbots can be more effective at social engineering than human scammers, WIRED reports. The researchers looked at a form of romance scam commonly known as “pig butchering,” in which scammers spend weeks or months building a relationship with the victim before tricking them into sending money for a phony investment scheme.
Donation Forms Attract Card Testing Attacks

A charity notices something odd in its payment dashboard. Hundreds of one dollar donations attempted overnight. Almost all declined. A handful approved. Nobody donated anything. The organization was being used as a validation service. Donation forms have become a preferred target for card testing, and the reasons are structural rather than accidental. Here is how the attack works, why nonprofit payment pages are disproportionately attractive, and what actually stops it.

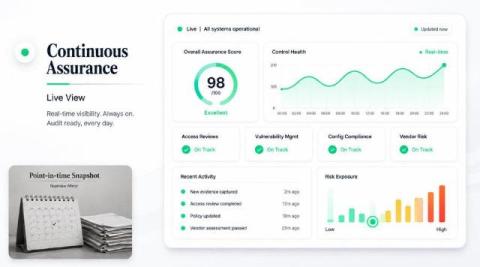
Legacy GRC can't keep up. Cyber risk assurance can.

Enterprise security teams need to secure a risk surface that is constantly changing. However, the tools in their stack were built to check only a fraction of that risk. For confirmation, they rely on static snapshots and annual attestations. I now see this as the defining problem in GRC. When 451 Research (S&P Global) initiated coverage of TrustCloud in this space, they described a clear and growing divide.

Top 14 Agent Observability Tools

Agent observability tools capture traces, metrics, logs, and evaluations across AI agent workflows. They help teams reconstruct execution paths, inspect tool calls and handoffs, diagnose failures, and monitor latency, cost, and output quality. This guide also covers complementary security platforms that discover agents, enforce runtime policies, or control the privileges agents receive. Agents don’t fail in straight lines.

One Loss Distribution, Two Very Different Charts

A cyber loss model produces one distribution. How that distribution gets drawn changes what a reader can see in it, and the conventional projection hides the part most decisions depend on. ‍ The two views below contain identical data. One of them is close to unreadable for anything except the extreme tail, and the difference is worth understanding before the next time somebody asks what the number means. ‍

Human in the Loop: How to Tell If the Review Is Real

Human oversight is the only control in an AI program that can stop working while producing exactly the same evidence as when it worked. A failed encryption control throws errors. A monitoring pipeline that breaks stops delivering alerts. A review step that has become a formality still generates approvals, timestamps and sign-offs, and the compliance file looks identical. ‍ The asymmetry makes the design question secondary to the measurement one.

What Is Noise Reduction in SIEM and Security Monitoring

A SOC analyst starts a shift with a queue full of alerts. The first few investigations reveal repeated authentication failures from the same service account, blocked network scans from a known internal scanner, and endpoint events that three different sensors reported separately. Somewhere in that queue may be a real compromise, but the analyst has to work through the noise before finding it.

PoshC2 Explained: Capabilities, Indicators, and Detection

PoshC2 version 6.0, an open-source command and control framework, is notable for its robust capabilities in managing compromised hosts. Accompanying its release, a comprehensive list of Indicators of Compromise (IoCs) and a dedicated GitHub repository have been provided. These resources are designed to assist cybersecurity teams in detecting PoshC2, especially when deployed with its default settings, which less sophisticated attackers often utilize.

Living Off the Land Attacks: Detection and Response Guide

The most popular advice about living off the land attacks is also the least useful when it stands alone: hunt for suspicious PowerShell, block LOLBins, and alert whenever a signed Microsoft binary behaves unexpectedly. Those controls have value, but they don't solve the operational problem. PowerShell, WMI, certutil.exe, and bitsadmin.exe are legitimate administrative utilities, and attackers abuse them precisely because security teams can't remove them without disrupting normal work.