Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Best AI security tools for small and mid-sized businesses in 2026

The best AI security tools for small and mid-sized businesses do more than detect risky AI use: they show which generative AI tools employees actually use, they let you govern which AI apps are allowed, monitored or blocked, they stop sensitive data from leaving in a prompt, and they defend against harmful prompts, including prompt injection. Most organizations now run AI without that visibility or control. AI use has moved into the mainstream.

How to Prevent RBAC Role Explosion with Nested Access Lists

In RBAC (Role-based Access Control), a role is a defined object with explicit permissions attached to it. Because roles are designed to be fixed, changing what a particular role can do (for example, in a one-off situation where other permissions are needed for the role) requires editing the role itself. However, repeatedly editing roles makes them less flexible and re-usable, and ultimately complicates access strategies as organizations scale.

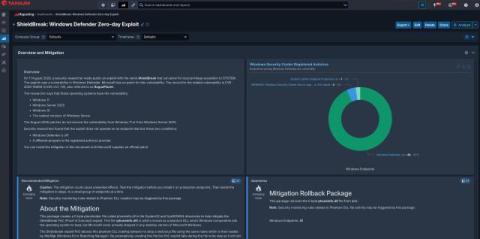
ShieldBreak: The Windows Defender 0-Day with No Patch - And What to Do About It.

In mid-June 2026, Microsoft acknowledged RoguePlanet, a privilege-escalation flaw in the Microsoft Malware Protection Engine (mpengine.dll), the scanning engine behind Windows Defender. Microsoft rated it "Exploitation More Likely" on its Exploitability Index and assigned a CVSS score of 7.8. Microsoft shipped a fix in Malware Protection Engine version 1.1.26060.3008 during its July 2026 patch cycle.

AI Is Accelerating Vulnerability Discovery. Tanium Helps You Keep Up.

Following the Mythos announcement in April 2026, organizations using AI to identify software vulnerabilities have contributed to a significant rise in newly discovered CVEs and CVE definitions. This shift reflects a broader trend across the industry: AI is helping uncover vulnerabilities faster than ever before — and security teams need the visibility, control, and speed to respond. At Tanium, we've been tracking this trend closely across customer environments.

The Top 5 Exposure Assessment Platforms (EAP) in 2026

An Exposure Assessment Platform (EAP) discovers assets, identifies exposures such as vulnerabilities and misconfigurations, prioritizes them with threat and business context, and helps drive remediation. Gartner formalized EAPs as a distinct market in November 2025, and the category has quickly become the technology backbone of Continuous Threat Exposure Management (CTEM) programs.

Can You Download Private Instagram Videos? The Honest Answer

Search for 'private Instagram downloader' and you'll find dozens of sites claiming to do it. Most of them can't - and the ones that claim otherwise are usually either misleading or asking for something you shouldn't give them (like your Instagram password). The honest answer depends on which specific situation you're in. Here's the full picture, without the misleading promises - and where a free instagram downloader actually works.

What No-KYC Hosting Actually Means

No-KYC hosting generally refers to hosting providers that allow customers to open an account without submitting government-issued identification or other standard KYC documents. Depending on the provider, however, verification may still be triggered later by a payment issue, abuse report, or legal requirement. The term gets thrown around loosely, sometimes implying total anonymity, sometimes just meaning "no ID upload form," and the difference between those two things matters more than it first appears.

Why Securing AI Agents Is More Critical Than Ever

AI agents offer unprecedented capabilities, speed, automation, deep context, and hyper-personalization, that will transform how we work. However, these same capabilities make AI agents significantly more dangerous than traditional software when hijacked by cybercriminals. You simply cannot rely on yesterday's risk management playbooks to handle today's AI-driven threats.

Report: Employees Are Overconfident in Their Ability to Spot Scams

A survey from Trustmi found that most employees believe they’d be able to spot a social engineering attack, but those same employees still rely primarily on outdated guidance to spot red flags. Generative AI has given attackers the ability to craft extremely convincing, error-free phishing emails.

Emerging Threat: (CVE-2026-72766) n8n Arbitrary File Read and SSRF via Send Email Node

CVE-2026-72766 is a type confusion vulnerability in the Send Email node of n8n, an open-source workflow automation platform. The node does not enforce that its message fields hold string values, so a non-string value arriving from a workflow expression can be passed through to the underlying mail library, Nodemailer, which interprets it as a file path or a URL rather than message text. The vulnerability carries a CVSS v3.1 base score of 7.5 (High). Under CVSS v4.0 it scores 8.2 (High).