General Data Protection Regulation (GDPR) is a framework for data protection that gives strict obligations for organizations within the European Union. For many businesses, understanding and implementing GDPR vendor management is a daunting task. That’s why we are going to break down what GDPR vendor management is, who is involved in it, and what the requirements are.
The GDPR compliance has the most rigorous privacy policies and security laws. It’s origin is in the EU. However, every cloud-hosted company has to comply with it to conduct business with EU citizens.
With the advent of the Digital Personal Data Protection Act (DPDP Act) in 2023, India has taken a significant step towards safeguarding the rights of individuals, termed as ‘Data Principals’, over their personal data. This blog post aims to shed light on the rights and protections offered to Data Principals under the DPDP Act, a landmark legislation that is reshaping the landscape of data privacy in India.
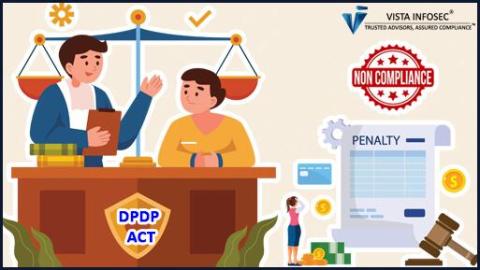
In the dynamic realm of data protection, understanding the consequences of non-compliance is crucial. The Digital Personal Data Protection (DPDP) Act of 2023 has set forth stringent penalties for those who fail to adhere to its provisions. We’ve delved into this new act in our series of blog posts.
With many nuances to consider, adhering to the General Data Protection Regulation (GDPR) requirements can be a daunting task. After all, the entirety of the GDPR consists of a whopping 99 Articles. Fortunately, by following a GDPR security checklist, you can help your organization ensure that all required facets of data security are covered without sifting through pages and pages of legalese.
Do you remember where you were on 25th May 2018? Perhaps you were enjoying a Friday night drink with friends. Perhaps you were with family, relaxing after a busy week at work. I was actually having a GDPR Birthday party with friends and colleagues because 25th May 2018 was a landmark day for the world of Data Protection (yes, seriously, we had a party!). But the funny thing about the effective date of the then-new General Data Protection Regulation (GDPR) was that many saw it as a date to dread.