Elastic Compute Cloud (EC2) is an Amazon Web Services (AWS) hosting service that extends scalable and secure virtual computing systems known as instances. They allow users to have their applications hosted in a scalable environment whereby computing resources can be easily scaled up or down as necessary. EC2 provides several instance types that can handle a variety of uses, from general-purpose and compute instances to those designed for memory-intensive applications.
Understanding the cost of deploying a Hugging Face model involves considering compute requirements, inference time, and hardware pricing. Let’s break it down.
What if the very core of your company—the digital ecosystem you painstakingly built—is under attack? If an invisible enemy gets illegal access and begins manipulating data or disrupting essential processes, your entire organization could be paralyzed in an instant. Remote Code Execution (RCE) vulnerabilities have this terrifying reality. RCEs are the holy grail for hackers, allowing them to run arbitrary commands on a target machine.
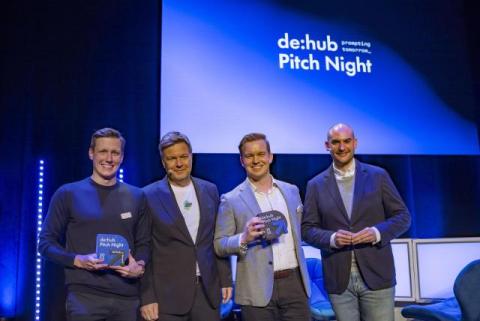
At the 6th de:hub Pitch Night, an event celebrating innovation and digital transformation, Code Intelligence was honored with the prestigious German AI Award. This recognition, awarded by a distinguished jury of industry experts and investors, underscores Code Intelligence’s pivotal role in advancing software security through artificial intelligence.
Cybercrime affects over 5 million individuals in the UK every year, with a majority living in London. This densely populated area is unsurprisingly a hotspot for cybercriminal activity. It’s one of the world’s leading financial and technological hubs, with thousands of Londoners experiencing cybercrimes such as scams, hacked accounts, and intimate image abuse annually.
Learn how one of Europe's largest healthcare tech leaders transformed their Secrets Security with GitGuardian, cutting incidents by half without compromising developer productivity.
Cyber security threats are increasingly complex, and while external attacks like phishing and malware often take centre stage, insider threats are emerging as a significant concern. Insider threats are risks originating from within an organisation, which pose unique challenges. They exploit an insider’s knowledge of systems, processes, and vulnerabilities, making detection and prevention particularly challenging.
If you work in application security, you’re probably familiar with the OWASP Top 10. But open-source frameworks like those maintained by OWASP members have a lot to offer security practitioners. In this episode of the Cybersecurity Sessions podcast, Netacea CISO Andy Ash meets OWASP Global Board Member and London Chapter Leader Sam Stepanyan to find out how Sam got involved with OWASP, and the influence it has on the security world.