Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Canada Raises the Bar for Critical Infrastructure Cybersecurity. Is Your Network Ready?

Canada has taken a significant step toward strengthening national cyber resilience. With Royal Assent now granted to Bill C-8, the Government of Canada is establishing a new framework for protecting critical cyber systems and securing the country's most essential services.

Investigate your network in plain English: introducing Natural Language Query

Every SOC analyst has been there. An alert fires. You know what you need to find. Maybe it's all outbound connections from a specific host that spiked overnight. Maybe it's every DNS query over 100 characters from a subnet you're watching. You know the question. What you don't know is the exact query syntax you need to ask it. So you open the documentation. You search for field names. You try a query, get it wrong, adjust, and try again. Minutes pass.

Post-Quantum Cryptography: The upgrade nobody asked for (but everyone's getting)

Post-Quantum Cryptography (PQC) is the security equivalent of showing up at the airport and discovering TSA changed the rules overnight again: Laptops out, laptops in, shoes off, shoes on, and declare your shampoo like it’s contraband uranium. You can argue with the signage, but the plane is still leaving, and compliance is not optional. The good news is you don’t need a physics degree, a quantum computer, or a wellness crystal to deal with it.

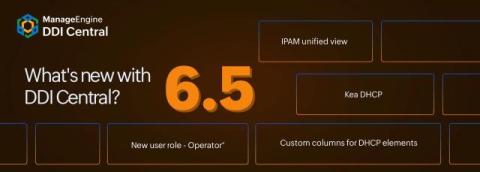
DDI Central 6500: Modern DHCP, unified visibility, and layered access control

DDI Central's release 6300 focused on authentication and identity: GSS-TSIG for secure DNS updates, LDAP/LDAPS-based user provisioning, and native Windows scavenging. Each aimed at cutting down the manual work behind keeping DNS and user access clean. DDI Central 6500 shifts focus elsewhere.

What CVE-2026-20079 Means for Every Network Team

On September 9, Cisco confirmed what earlier warning signs had already hinted at: a security flaw in its Secure Firewall Management Center (Secure FMC) software, the tool that configures and controls Cisco firewalls across a network, is being actively exploited. The flaw, tracked as CVE-2026-20079, received a maximum severity score of 10.0 on the CVSS scale, the industry-standard scale used to rate how serious a vulnerability is.

Securing what your Bedrock AgentCore agents actually do

An AI agent is software that can act on your behalf. It may read documents, emails, and web pages, then use the systems you connected to complete a task. Amazon Bedrock AgentCore makes these agents faster to build and deploy. But securing them requires more than limiting which systems an agent can access. You also need to consider what the agent can read once it gets there. A document, email, or web page may contain hidden or malicious instructions designed to influence an agent’s next action.

The water system attacks were simple. Securing OT isn't.

Recent cyberattacks against U.S. water and wastewater systems have put some familiar operational technology (OT) security problems back in the headlines. Federal agencies have warned about malicious actors targeting internet-facing programmable logic controllers (PLCs), changing device configurations, and disrupting operations at utilities across multiple states.

Claude Mythos Explained: AI Finding Zero-Day Vulnerabilities and Chaining Exploits

Claude Mythos is an AI model capable of finding and chaining zero-day vulnerabilities at scale. That changes how attacks happen, especially in environments where you can’t patch fast enough. The Forescout Vistaro platform with VistaroAI helps organizations respond with real-time visibility and dynamic control across all connected devices.