Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

WAF vs WAAP API vs AI What Security Tools Do You Actually Need?

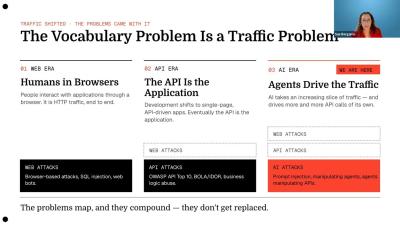
A straightforward framework for matching each layer of protection to the problem it actually solves. Trying to understand vendors in the modern application security space can feel a lot like trying to solve word scramble. Whether it’s remembering what the “A’s” in "WAAP” stand for, figuring out if “WAF” includes APIs, or assessing the actual function of a new AI security product, understanding what tools your team actually needs is getting harder all the time.
How to Make Smart Security Decisions in the AI Era

AI is changing the speed and scale of cyber risk, but the fundamentals of security remain the same. Elisa Costante, VP of Software Engineering at Forescout, discusses why visibility, risk assessment, and adaptive controls are essential for protecting organizations against rapidly evolving threats. Learn more.

How Early Action Helps Organizations Stay Ahead

In a rapidly changing technology landscape, waiting for consensus can mean losing the advantage. Elisa Costante, VP of Software Engineering at Forescout, explains how acting early helps organizations build understanding, adapt to change, and stay ahead as AI transforms cybersecurity for defenders and attackers alike.

CVSS Measures Severity. Risk Requires Context.

CVSS remains a valuable tool for understanding vulnerability severity, but severity and risk are not the same. In this video, we explore why effective risk management requires additional context, including asset reachability, business impact, remediation timelines, and an organization's ability to reduce exposure. CVSS can help start the conversation, but it shouldn't be the only factor driving prioritization decisions.

CVSS Scores Alone Can Mislead Vulnerability Prioritization

Not every high-severity vulnerability represents the highest risk. Learn why effective prioritization requires more than a CVSS score and how factors such as reachability, exploitability, active exploitation, and asset criticality provide the context needed to focus remediation efforts where they matter most.

PQC Post Quantum Cryptography Explained: Why Today's Encryption Has an Expiration Date

The encryption protecting today’s data isn’t broken, but it does have a timeline. This video breaks down why current systems like TLS, PKI, and RSA remain secure today, and how quantum computing will change that. As progress accelerates toward large-scale quantum machines, organizations must prepare for a new era of security. Learn how PQC (post-quantum cryptography) helps address emerging risks like “harvest now, decrypt later,” and why tracking adoption of quantum-safe encryption is critical now, not later.

Recognizing and detecting data exfiltration

Every breach that lands a CISO in front of the board has a common final act: Data leaving the building. Attackers don't get paid for breaking in. They get paid for what they take out. And by the time stolen data appears on an extortion site or in a regulator's inbox, the window to stop the damage has already closed. That is what makes exfiltration so dangerous. It rarely looks like an emergency.