Critical zero-day Citrix CVE-2023-3519 is still being exploited two months after Citrix released a patch. IONIX research found that 19% of the CVE-2023-3519 vulnerabilities are still unmitigated in comparison to only 3% among IONIX customers. In addition, IONIX customers were able to resolve this critical risk three times faster.
At the start of 2022, CrowdStrike Intelligence and CrowdStrike Services investigated an incident in which PROPHET SPIDER exploited CVE-2021-22941 — a remote code execution (RCE) vulnerability impacting Citrix ShareFile Storage Zones Controller — to compromise a Microsoft Internet Information Services (IIS) web server. The adversary exploited the vulnerability to deploy a webshell that enabled the downloading of additional tools.
CurrentWare’s suite of user activity monitoring, web filtering, device control, and remote PC power management software has been verified as Citrix Ready®. The Citrix Ready program helps users of Citrix Virtual Apps and Desktops (formerly Citrix XenApp and XenDesktop) identify third-party solutions that are verified as compatible with a Citrix VDI deployment.
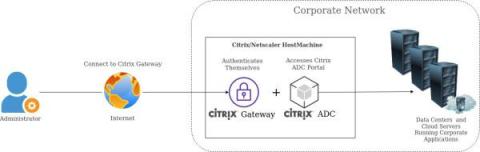
In December 2019, Citrix announced that their flagship product, Citrix Application Delivery Controller (ADC) and Gateway, had a vulnerability that would allow code execution to take place on affected devices without any authentication. This vulnerability (designated CVE-2019-19781) was severe - on a scale of 1 to 10 it was deemed a 9.8 meaning that an attacker able to exploit this vulnerability could do serious damage.
Last updated: 20th January, 9.45am. A critical Citrix vulnerability (CVE-2019-19781) is currently under mass exploitation. To detect if your organisation is compromised, Redscan has developed a script that will examine your host.