Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Persona Research investigates big questions in online identity

Persona Research studies identity and trust. We advance methods for making online identity verification safer, fairer, and more accurate. We think this work is important because identity is fundamental to how people access services, form communities, and participate online. And we want to protect people without limiting their agency or access. Timestamps: Read more about Persona's research team, publications, and grant program: research.withpersona.com.
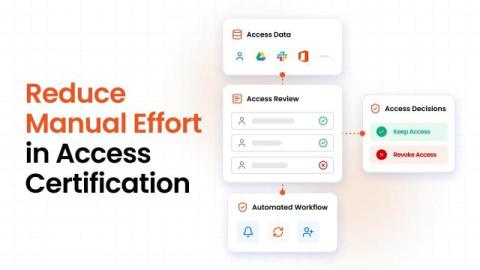
How to Reduce Manual Effort in Access Certification

Access certification can take more time than the actual review. A manager may need to review access for 50 employees. Before that happens, someone has to gather the access data, identify the right reviewer, send the requests, and track the responses. If the reviewer revokes access, someone may also need to remove it from the application. Now repeat that across hundreds of users and several applications. The workload adds up quickly.

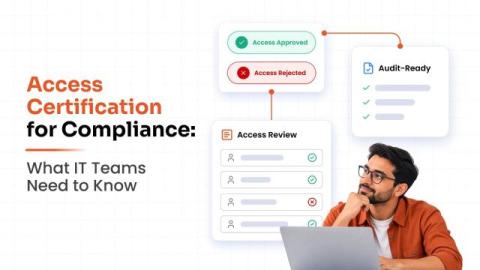
Access Certification For Compliance: What IT Teams Need To Know

An access review can look complete on paper. The campaign closed, reviewers made their decisions, and the records were saved. Then an auditor asks: Who reviewed this access, what did they decide, and what happened afterward? That question can reveal problems that a completed review does not show. A rejected permission may still be active. An exception may have no clear reason. The team may also struggle to show when the review happened.

Non-Human Identity Management in Atlassian Cloud

Ask a security team how many employees they have and they will answer instantly. Ask how many non-human identities they have, and the room goes quiet. Non-human identities (NHIs) are the identities that applications, services and automation use to act in a system. Service accounts, automation users and bot logins are identities, while API tokens, keys and certificates are the credentials they authenticate with, and teams have to govern both. These identities run deployments, sync data, post notifications and generate reports, usually without anyone watching.

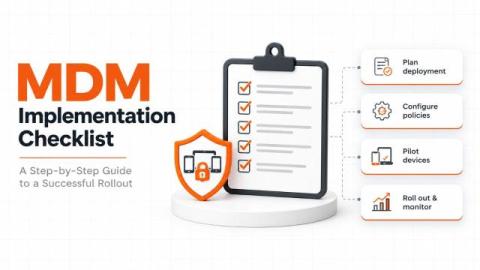
MDM Implementation Checklist: From Planning to Deployment

Enrolling devices is only one part of implementing Mobile Device Management (MDM). Before rollout, IT teams need to define ownership models, prepare the environment, configure policies, and verify that employees can access the apps and resources they need. This MDM implementation checklist breaks the process into seven phases, from initial planning to ongoing device management. Use it to organize responsibilities, identify dependencies, and confirm that each phase is ready before moving to the next.

Session on From Pink City to Tech City: Jaipur's WordPress and AI Future at Rajasthan WordCamp 2026

In this Session at WordCamp Rajasthan 2026, Rajasthan International Centre, Jaipur, our Founder & CEO, Mr. Anirban Mukherji, discussed the future of Jaipur’s technology landscape and the growing opportunities in WordPress, artificial intelligence, cybersecurity, and software innovation.

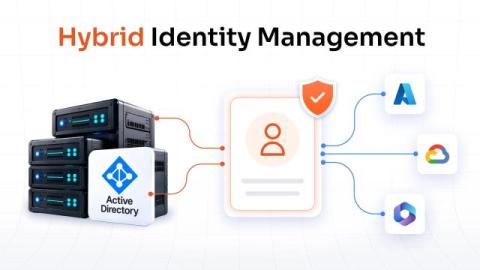
Hybrid Identity Management: Secure Access Across Cloud and On-Premises

Hybrid identity management is the practice of managing user identities and access across on-premises and cloud environments through a connected identity framework. Most organizations today operate across both. Active Directory may still manage identities for internal applications, while cloud platforms and SaaS applications handle other parts of the business. This creates a simple challenge: how do you give users consistent access when their applications and identities exist in different environments?

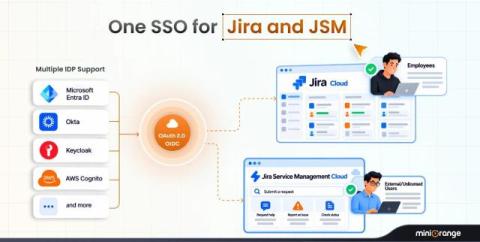
Why OAuth SSO Matters for Both Jira Cloud and Jira Service Management

Jira is rarely used by just one type of user. Primarily, teams use Jira Cloud for project management. At the same time, support teams work inside Jira Service Management (JSM), while internal employees and external users such as customers, vendors, and partners may access the JSM portal. They are all accessing the same Atlassian ecosystem, but they do not necessarily log in the same way. This is where organizations can run into a problem.

One Identity: Governing Every Identity - Human, Machine, and AI

Every enterprise runs on identity — and machines and AI agents now outnumber people in many environments. This 2-minute overview covers why identity has become a board-level priority, and how One Identity governs every identity — human, machine, and AI agent — on one unified platform. Validated by Omdia: 150% ROI, go-live in as little as one day, zero-touch onboarding.

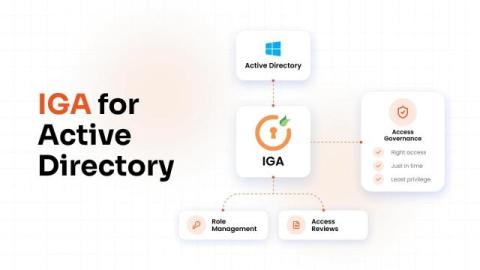
Active Directory Governance: How to Know Who Has Access and Why

An employee changes roles. Their manager requests access for the new job, and IT grants it quickly. That part works well. The issue appears when access from the previous role stays in place. The same thing happens when a contractor finishes a project, an admin completes urgent work, or a team retires an application. Access often remains because nobody has checked whether it still serves a purpose. Active Directory governance allows IT and security teams to answer three questions.