Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

User Access Management: Process, Controls, and Benefits Explained

Access sprawl is quiet. For example, a contractor's admin rights outlive the project by eight months, or an account sits open for weeks after someone switches teams. And in most cases, nobody catches access sprawl until an audit or a breach forces the question. User access management (UAM) is the discipline that catches this. It decides who gets access to what, why they get it, how that access is approved, how it changes over time, and when it gets pulled.
Beyond the Login Screen: Why Qualified Electronic Signatures Belong in Identity Security

For years, identity security was mostly discussed as an access problem. Can the right person log in? Is multi-factor authentication enabled? Are privileged accounts protected? Can stolen credentials be used from an unknown device? Those questions still matter. But they describe only the beginning of a digital transaction.

SSH Session Monitoring: How to Monitor, Record & Audit SSH Sessions

Secure Shell (SSH) gives you direct access to critical servers, databases, and cloud infrastructure. Once a privileged user connects through SSH, they hold extensive control over that system. They can alter core configurations, run terminal scripts, move files, or delete production databases in seconds. If you lack visibility into privileged actions, it can be risky. If a credential gets stolen or an insider goes rogue, traditional firewalls won’t be enough.

How Is AI Transforming Identity and Access Management?

Traditional Identity and Access Management (IAM) relies on authentication methods, predefined roles, and access policies to control who can access business applications and data. These controls remain essential, but they do not always provide enough context to identify unusual behavior or changing access risks. AI in Identity and Access Management (IAM) adds another layer of intelligence by analyzing login context, user behavior, device information, access patterns, and identity activity.

MFA for Telecommunications: Securing Networks, Admins, and Customer Accounts

A single telecom login is one of the most dangerous keys in existence. Behind it sit subscriber identities, billing systems, and the network backbone every other industry depends on. In April 2025, SK Telecom admitted attackers had stolen authentication records tied to its USIM cards, affecting 27 million subscribers, with malware present for years before discovery. Weeks earlier, the FBI warned of a campaign using AI-generated voice and text to trick targets into handing over account access.

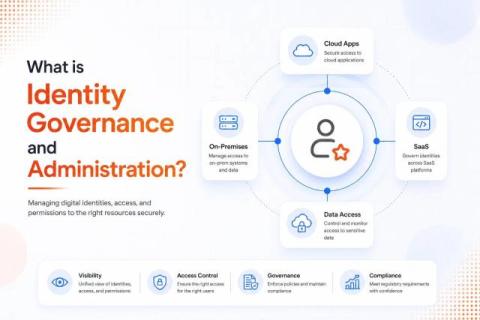
What is Identity Governance and Administration (IGA)?

Enterprises today manage thousands of identities across employees, contractors, applications, APIs, and machine-driven systems. In most environments, identities have become the primary security boundary, yet access remains fragmented, overprovisioned, and difficult to track. According to IBM's X-Force Threat Intelligence Index, identity-based attacks now account for nearly one-third of all intrusions, highlighting how identity has become one of the most targeted layers in modern cybersecurity.

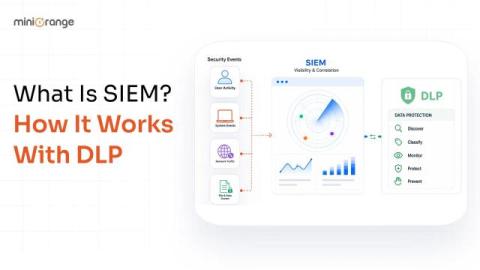
What Is SIEM? How It Works With DLP to Detect Data Threats

Most security teams don’t lose the fight against data breaches because they lack tools. They lose because their tools don’t talk to each other. This is exactly the loophole that SIEM and DLP were built to close, together. Security information and event management gives you visibility into what’s happening across your entire environment. At the same time, data loss prevention gives you the control to stop sensitive information from leaving in the first place.

One Identity CEO talks winning CISO board pitch & identity fabric

Breaches will impact an organization greatly, regardless of industry or your role in it, and Larry Chinski, VP of enterprise strategy, caught up with CEO Praerit Garg to explore the challenges facing CISOs in trying to communicate this fact. Tune in for insights on learning to speak the ROI-focused language of the board when pitching a security budget. And keep watching for a discussion on the benefits behind a comprehensive identity fabric for your identity security.

What Is MFA for Air-Gapped Networks? Closing the Last Security Gap in Isolated Systems

Air-gapped networks are supposed to be untouchable. No internet connection, no remote pathway, no way in for an attacker sitting halfway across the world. But ask any security team that has actually run one of these environments, and you'll hear a different story. Air gaps stop remote attacks cold. But they do almost nothing to stop a stolen password, a careless USB stick, or an insider with too much trust and too little oversight. That's the gap, and Multi-Factor Authentication (MFA) is here to fill it.