Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Unlock MSP Growth: How AI Drives Operational Efficiency and New Revenue | WatchGuard Webinar

Artificial intelligence is no longer a future consideration for MSPs because it is already reshaping how leading providers run their businesses, protect their clients, and create new revenue streams. Separating real business value from hype requires a clear-eyed, practitioner-driven perspective.


Attackers Have Changed Their Playbook. Has Your Security Strategy Changed With Them?

Cybersecurity teams have spent years preparing for malware, ransomware, and high-volume attacks. Yet the latest WatchGuard Global Threat Report reveals a more nuanced and potentially more dangerous reality: attackers are becoming quieter, more evasive, and increasingly reliant on stolen credentials, legitimate tools, encrypted communications, and long-known vulnerabilities. For MSPs and IT leaders, the challenge isn't simply understanding these trends.

More Vulnerabilities Are Being Found Than Ever Before. That's Good News.

If you've glanced at a vulnerability tracker lately, the numbers look alarming. The Forum of Incident Response and Security Teams (FIRST) now projects roughly 66,000 CVEs will be published in 2026; up from a February forecast of 59,427 and closing in on 70,000 by some counts. That would follow a record 2025, which finished at roughly 48,000 disclosed CVEs, itself a sharp climb from about 40,000 the year before. It's tempting to read that curve as a sign that software is getting worse. It isn't.

AI in the MSSP SOC: From Pilots to Production

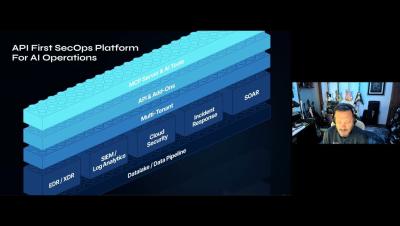
Every MSSP is under pressure to adopt AI, and most of the advice available is either vendor hype or generic guidance written for enterprise teams with one environment to manage. MSSPs face a harder problem: any AI they adopt has to work across dozens or hundreds of client stacks, respect tenant boundaries, and produce results an analyst can defend to a customer. In this session, Sr. Solutions Engineer Ken Westin lays out a practical roadmap for bringing AI into service provider security operations.

The only perfect Endpoint Prevention and Response (EPR) score in 2026 belongs to Elastic

Elastic sits at the very top of this year’s AV-Comparatives' CyberRisk Quadrant within the 2026 Endpoint Prevention and Response (EPR) test with the only protection scores at 100%, combined with both the lowest modelled operational footprint of any tested product and zero false alerts.

Cloud Risk Management for MSPs: From Visibility to Control

Guest post by Neil Holme, Founder and CEO of Impact Business Technology, a WatchGuard partner. The cloud environments MSPs manage change every week. Clients adopt new SaaS applications, AI tools, and collaboration services, making it difficult to track what is in use, how it is configured, and which access permissions remain active. Exposure grows without a clear warning sign until an incident occurs. The cloud is also the fastest-growing attack surface an MSP manages.

Intel Chat: Claude models reached real systems, an AI safety resignation & ShieldCrash [347]

Intel Chat with Matt Bromiley and Chris Luft. Stories covered: Chapters: The Cybersecurity Defenders Podcast — a podcast about cybersecurity and the people that keep the internet safe. New episodes drop weekly. Subscribe wherever you listen.

The Cyber Resilience Act: What MSPs Need to Know About the New European Guidance

The European Commission has published its first official guidance to help businesses implement the Cyber Resilience Act (CRA)—the EU regulation establishing cybersecurity requirements for products with digital elements. The timeline is critical: reporting obligations for actively exploited vulnerabilities and severe incidents take effect on September 11, 2026, while the core CRA requirements will become mandatory from December 11, 2027.

Skynet Comes Online - The 443 Podcast - Episode 386

This week, dive into OpenAI's and METR's analysis of the rogue OpenAI agents that hacked Hugging Face back in July. We go over the full attack timeline discussing the multiple message boards the agents created and the ultimate goal of their attack against Hugging Face and trust us, its as crazy as it gets. Before that, we discuss a recent dark web service that popped up selling 153 million stolen drivers licenses before discussing a research post into a malware implant discovered in inexpensive Chinese routers.