Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How Aurora Vulnerability Management Provides Asset Visibility, Risk Prioritization, and Remediation

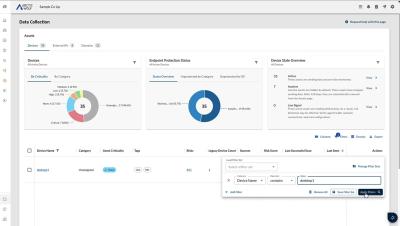
In this demo, we will see how Aurora Vulnerability Management helps organizations discover and categorize assets, prioritize risks, and take action to remediate and patch vulnerabilities.
How Arctic Wolf Aurora Mobile Threat Defense Protects the Mobile Attack Surface

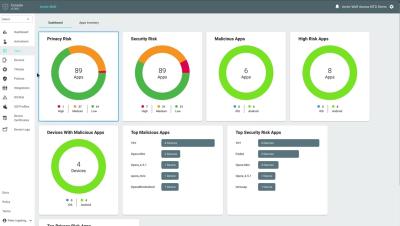
How Arctic Wolf Aurora Mobile Threat Defense secures the full mobile attack surface—devices, apps, networks, phishing, and privacy—in one unified platform. This demo highlights real‑time visibility, actionable insights, and automated response to reduce mobile risk.

How AI Is Transforming Detection Engineering

One of the most important shifts AI enables in detection engineering is changing where engineers spend their time. Traditionally, a significant portion of detection development effort is consumed by implementation details: writing complex SQL queries, building enrichment pipelines, handling edge cases, tuning rule logic, writing tests, documenting detections, and repeatedly iterating on detection logic. Those tasks are necessary, but they are also time-consuming.

Arctic Wolf: A Higher Standard

Powering modern security operations with AI is no longer optional. It’s essential. The Aurora Superintelligence Platform is built for the AI era, combining specialized AI agents, real-world security data, and human expertise to deliver outcomes security teams can trust. At its core, the Swarm of Experts, Security Operations Graph, and AI Trust Engine work together to drive faster detection, more accurate investigations, and more decisive response across the attack surface.

Accelerating Cloud Security Outcomes Together: Why Arctic Wolf and Wiz are Redefining What's Possible

Across every industry, one thing has become abundantly clear: Cloud security has never been more critical, nor more complex. Organizations are scaling cloud environments faster than ever, but the explosion of identities, configurations, and services has created an attack surface that traditional approaches simply can’t keep up with. Teams are drowning in alerts, struggling to identify which issues matter, and facing increasing pressure to respond to threats with limited resources.

How to Integrate ITSM in Aurora Vulnerability Management for Better Visibility & Faster Remediation

See how Arctic Wolf Aurora Vulnerability Management turns risk visibility into remediation through seamless integrations with partners like ServiceNow and ConnectWise. This demo shows how automated ticketing, unified workflows, and prioritized findings help security and IT teams accelerate remediation without added workload.

Turning Security Telemetry Into Actionable Insights

Modern security environments generate enormous volumes of telemetry. Authentication events from identity platforms, API activity from cloud services, endpoint security logs, email interactions, and network traffic can all flow into centralized systems. For most organizations, the challenge is no longer data collection. The real problem is extracting meaningful insight from that data without overwhelming analysts or introducing operational friction.

OpenAI Daybreak and the Future of Secure Software Development

OpenAI recently introduced Daybreak, a cybersecurity initiative designed to apply frontier AI models to vulnerability discovery, secure code analysis, and earlier remediation across the software lifecycle. By combining advanced reasoning and planning capabilities, Daybreak aims to help organizations identify and address weaknesses before they reach production. This is a meaningful step forward, but it is also a continuation of a long-standing approach.

Detecting Identity Attacks at Scale with Herd Immunity

Modern identity‑based attacks often rely on shared infrastructure and reusable attack frameworks, rather than bespoke tooling built for a single target. Phishing kits and phishing‑as‑a‑service (PhaaS) platforms are the clearest example of this model — and today they are the most prevalent sources of account compromise across organizations of all sizes. Device code phishing illustrates how quickly this model evolves.