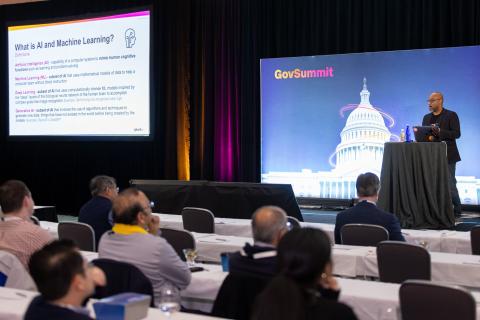
The role of governments has evolved to include the safeguarding of not just physical borders but also virtual territories. With an increasing reliance on technology, the need for robust cybersecurity measures within government entities has never been more critical. Here we’ll explore cybersecurity best practices that can fortify government systems, ensuring the protection of sensitive information and the preservation of national security.
Protecting sensitive data from the threat of exposure is a non-negotiable business imperative for organizations, especially those in highly regulated sectors like government and healthcare. To help organizations keep their data secure, the National Institute of Science and Technology (NIST) developed a set of requirements for the hardware and software components responsible for data encryption.
As government agencies accelerate their adoption of cloud technologies—particularly SaaS applications—they need to adhere to strict compliance and security standards. The Federal Risk and Authorization Management Program (FedRAMP) sets these standards for civilian federal agencies, while the Impact Levels laid out by the Defense Information Systems Agency (DISA) in their Cloud Computing Security Requirements Guide set guidelines for Department of Defense (DoD) agencies.
Protecting critical infrastructure has become an indispensable aspect of national security and public welfare. Critical infrastructure, encompassing essential systems such as power grids, transportation networks, water supply systems, and communication channels, forms the backbone of a nation’s economy, security, and health.
Keeper Security is excited to announce that our government solution, Keeper Security Government Cloud has been honored with three ASTORS Homeland Security Awards. The FedRAMP Authorized password and privileged access management platform was recognized for Best Cyber Security Solution, Best Privileged Access Security Solution and Best Cyber Encryption Solution at the annual ASTORS awards ceremony held in New York City.
Validating the security of your organization’s sensitive information at a single point in time with an annual risk assessment can be helpful, but what about the other 364 days of the year? If you have a cloud application and hope to sell your services to federal agencies, point-in-time assessments won’t be enough.
FedRAMP, which stands for Federal Risk and Authorization Management Program, is a U.S. government-wide program that standardizes the security assessment, authorization, and continuous monitoring processes for cloud products and services used by federal agencies. The goal of FedRAMP is to ensure the security of cloud-based systems and protect sensitive government data. Key objectives of FedRAMP include.