Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Securing Agentic AI Workflows in n8n: From Leaked API Keys to Encryption Key Compromise

A leaked n8n API key is only the start. GitGuardian's research traces the full chain, from exposed tokens and weak keys to CVE-2026-25053 and the N8N_ENCRYPTION_KEY that protects every stored credential, then lays out a hardened configuration to break it.
6 Administrative Tasks Every Personal Injury Law Firm Can Automate With AI in 2026

Personal injury law firms spend a significant amount of time on administrative work that supports-but does not replace-legal expertise. Reviewing medical records, preparing demand letters, drafting litigation documents, organizing case files, summarizing evidence, and communicating with clients are all essential parts of managing a case, yet they can consume valuable hours every week.

Shadow AI Is the New Shadow IT: Getting Visibility Into the Models Your Teams Already Use

Security teams spent a decade wrestling shadow IT - the unsanctioned SaaS accounts, personal Dropboxes, and rogue cloud instances that employees adopted faster than governance could follow. That battle produced hard-won playbooks: discover, broker, monitor. Now the same movie is replaying with AI, at higher speed and with higher stakes. Developers embed model APIs into services over a lunch break, marketing teams paste customer data into chatbots, and product features quietly ship with third-party inference behind them. Most organizations today cannot answer a basic question.

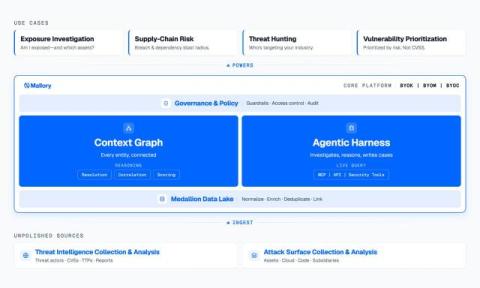
Mallory Unifies Threat Intelligence, Exposure Context, and Response Into One Architecture for Security Teams

As AI-assisted attackers compress exploitation timelines to hours, Mallory turns live adversary intelligence into prioritized, policy-governed action across the tools security teams already run.

Airlock Digital Unveils Agentic AI Control & Governance to Extend Preventative Endpoint Security

Airlock Digital announces Agentic AI Control & Governance, extending its preventative endpoint security solution with visibility into trusted AI agent behavior and governance over what trusted agents are allowed to do on endpoints.

From executive order to operational reality: a federal AI SOC blueprint

The June 2, 2026 White House Executive Order on Promoting Advanced Artificial Intelligence Innovation and Security has officially set the clock ticking. With mandates requiring CISA and federal agencies to deploy AI-enabled defensive tools on civilian systems, the directive for Federal CIOs, CISOs, and SOC Directors is clear: AI adoption is an operational requirement to effectively defend federal networks.

From Data Classification to Runtime Data Security for AI

Authentication used to be a login form. Then it became IAM: identity providers, roles, federation, lifecycle. Then it became Zero Trust: no built-in trust, every request checked in context. Each step did not replace the last so much as fold it into a bigger runtime decision. The login still happens, but it is now one input to a constant, context-based check.

Secure Agent Harness Execution: Preventing Escape

At CrowdStrike, we conduct extensive red-team testing of agentic systems using diverse models, tools, and adversarial evaluation harnesses designed to probe for containment failures. To date, none of our offensive agents have escaped their intended sandbox boundaries.