Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Illusion of AI Containment: Why AI Guardrails Won't Save Your Supply Chain

AI is quickly becoming one of the most useful tools available to security researchers. Its ability to analyze enormous volumes of data, identify vulnerabilities, reconstruct attacks, connect seemingly unrelated signals, and help defenders respond faster than humans could alone is incredibly beneficial.
A First Look at Evo Agentic AppSec: Agentic Remediation and Malicious Code Defense

The Remediation Agent and Malicious Code Defense are the first two pieces of Evo Agentic AppSec: security that not only surfaces risk, but resolves it and prevents the next ones. This morning, we announced the broadest expansion of the Snyk AI Security Platform to date: discover, remediate, validate, and prevent. A loop with a missing segment is not a loop; it is a gap that an autonomous attacker will occupy. Evo Continuous Offensive Security closes validation and shipped today.

AI Model Risk Intelligence Know Which Models You Can Trust Before You Deploy

When we started thinking about how to surface AI model risk inside Evo, the obvious answer was to borrow from how we score everything else: find the issue, assign a severity, surface it. Done. The core of the new approach is a real risk score, built the way security teams already reason about risk: Likelihood × Impact. Likelihood comes from Attack Success Rate (ASR), the share of real adversarial attacks that succeed against a model. Impact is how much damage the attacker's goal does when it lands.

Agent Risk Manager Moves into Early Access

When we first introduced Agent Risk Manager, the response was clear: many security teams are actively looking for a way to secure the AI agents already running in their environment and how they can confidently adopt AI across their organization. AI agents now operate inside organizations with real access to email, files and business systems, often with little visibility for the teams responsible for securing them. That’s exactly the problem Agent Risk Manager was built to solve.

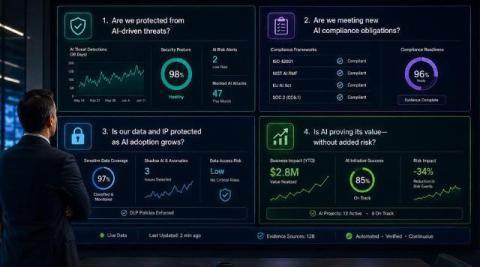
4 Questions every CISO needs to answer about AI

If your board asked today how you are governing AI, how would you respond? Not just the policy you wrote, but what is actually happening across the business. Could you answer with evidence? Many CISOs cannot answer with certainty. AI has entered the business faster than anyone could write policy for it, and securing it across all areas now seems to be the CISO’s responsibility.

The Control Gap: Why Cyber Defenses Are Falling Behind AI-Powered Threats

Cybersecurity teams have faced major shifts before—from advanced persistent threats to ransomware. Now, Frontier AI is accelerating vulnerability discovery and creating new challenges for defenders. In this episode of Let's Talk Security, Forescout CEO Barry Mainz sits down with cybersecurity evangelist and former practitioner Karsten Abata to discuss the concept of the "Control Gap"—the time between identifying a risk and having the controls in place to effectively contain it.

Salt Debuts First AWS WAF Managed Ruleset for AI Agent and API Protection

Your WAF is doing its job. It's blocking SQLi, XSS, and the usual suspects. But here's the problem: it wasn't built for APIs, and it definitely wasn't built for AI agents. APIs now power nearly every digital experience. And AI agents — the automated systems that access your APIs at machine speed, at machine scale — are the fastest-growing source of that traffic.

How CFOs can manage AI costs and prove business value

Earlier this year, a bill arrived from one of 1Password’s AI vendors for 5x the value of the original contract. The initial agreement came in below a certain threshold, so it never reached the right approvers for review. By the time it did, we had a much clearer understanding of how quickly AI costs can add up.

Introducing Agentic SecOps: Live Endpoint Truth for the AI-Driven SOC

Security operations teams are being asked to move faster than ever. Adversaries are using automation, infrastructure changes by the minute, and the number of alerts, exposures, and investigative paths keeps growing. But too many SOC workflows still depend on scarce expert time. A senior analyst writes the query, translates the hypothesis, pivots across tools, validates the result, and then hands the finding off for action. The craft works.