Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Human-AI Partnership: Securing the New Dual-Front of Business Risk

The integration of artificial intelligence into the modern workplace represents a paradigm shift in productivity and innovation. From desktops to mobile devices, AI agents are now deeply embedded in daily workflows, augmenting human intelligence and accelerating business processes at an unprecedented scale.
How Cybercriminals are using AI - and How to Defend Against It

What happens when the dark side gets its hands on cutting-edge AI — and why might even seasoned defenders find themselves playing catch-up? Welcome back to Razorwire, where I’m joined by Oliver Rochford and Richard Cassidy to discuss how criminals are using AI, what’s actually working and how the threat landscape is changing. We explore how adversaries are using AI, what’s actually working in the wild and how professionals can prepare for the unsettling pace of change.

Browser Agent Security Risk - ChatGPT Atlas Corporate Adoption Trends

Last Tuesday, October 21st, OpenAI released ChatGPT Atlas, an AI-powered browser that allows users to interact with ChatGPT directly from any browser tab. Throughout last week, the Cyberhaven Labs team tracked its adoption in corporate environments and actively investigated its security vulnerabilities.

When AI Joins the Cybercrime Underworld: How Far Ahead Are Hackers Now?

In this week's episode, discover how AI-driven attacks are rewriting the rules of cybersecurity. Phishing is nearly impossible to spot, deepfakes target companies, and self-evolving malware is changing the game. Meet the new adversary: artificial intelligence. Watch the full discussion in this week's show.

Meet Jit's AI Agents: The Future of Product Security Work

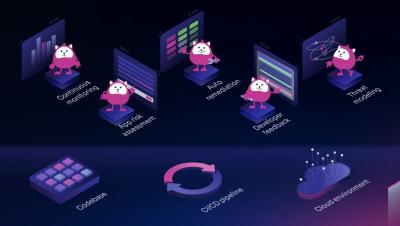
Application security has become too complex — too many scanners, too much noise, and not enough time. Jit’s AI Agents change that. Built on Jit’s Agentic ASPM Platform, these intelligent agents don’t just detect issues — they think like your best AppSec engineer. They correlate findings across systems, validate real attack paths, generate human-in-the-loop fixes, and continuously monitor what actually matters to your business.

Keeping the Internet fast and secure: introducing Merkle Tree Certificates

The world is in a race to build its first quantum computer capable of solving practical problems not feasible on even the largest conventional supercomputers. While the quantum computing paradigm promises many benefits, it also threatens the security of the Internet by breaking much of the cryptography we have come to rely on. To mitigate this threat, Cloudflare is helping to migrate the Internet to Post-Quantum (PQ) cryptography.

Making AI Less "Wednesday:" A Practical Guide to Using AI in Cyber Defense

Artificial intelligence has only been available for a relatively short period. Still, already many cyber defenders are as frightened as if Jenna Ortega’s Wednesday Addams had whipped her head around and set her dark, dangerous eyes on them. It’s not hard to see why. Machine learning, Gen AI, and Retrieval-Augmented Generation (RAG) are a few of more than 20 new acronyms flooding our industry, with more being added almost every day.

Unlock Deeper Insights: Mastering Cloudflare Log Explorer for Better Security & Performance

Cloudflare Log Explorer is the native observability and forensics tool designed to give security teams and developers unparalleled, granular access to Cloudflare traffic logs directly within the dashboard. Key benefits include: Understanding your traffic patterns is fundamental to optimizing for peak performance and maintaining a robust security posture.

Using LLMs to filter out false positives from static code analysis

Static application security testing (SAST) is foundational to modern application and code security programs. Yet these tools inevitably produce false positives that require manual review. When scanners find vulnerabilities that are not genuine issues, they erode trust, slow down remediation, and make it harder for teams to understand which alerts require attention.

The API vulnerabilities nobody talks about: excessive data exposure

TLDR: Excessive Data Exposure (leaking internal data via API responses) is the silent, pervasive threat that is more dangerous than single dramatic flaws like SQL Injection. It amplifies every other API vulnerability (like BOLA) and happens everywhere because developers prioritize speed over explicit data filtering. Fixing it means systematically checking hundreds of endpoints for unneeded PII and sensitive internal data.