Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Unveiling Top API Vulnerabilities and Emerging Trends: Introducing the Wallarm Q2 2024 API ThreatStats Report

As we move through 2024, the Wallarm Research Team continues to monitor the evolving API vulnerability and threat landscape. Our latest Q2 ThreatStats Report reveals critical trends and developments that are reshaping the security environment. Continuing from our Q1 findings, the surge in AI API vulnerabilities is not only persisting but intensifying, with an alarming increase in both the volume and severity of exploits.
Creating happier and more engaged teams with AI and workflow automation

High stakes, long hours, and a rapidly evolving threat landscape present unique barriers to happiness for security and IT teams. It’s not surprising that 63% of security practitioners report some level of burnout, and 58% of IT professionals feel overwhelmed by the amount of tasks they have to do in a day. Organizations simply can’t afford to ignore these statistics.

A wild week in phishing, and what it means for you

Being a bad guy on the Internet is a really good business. In more than 90% of cybersecurity incidents, phishing is the root cause of the attack, and during this third week of August phishing attacks were reported against the U.S. elections, in the geopolitical conflict between the U.S., Israel, and Iran, and to cause $60M in corporate losses.

Insights From The SOC

A review of AI-generated malware, and how a SOC might deal with the ever-increasing threat… Theofanis Dimakis, SOC Officer, and Nikolaos Tsompanidis, Threat Detection & Response Expert at Obrela, speaking during the recent CRESTCon Europe event, shared insights from their perspective into detecting malware, including the rising tide of AI variants.

Building for the Future DevSecOps in the era of AI ML Model Development

Melissa McKay, JFrog Developer Advocate, and Sunil Bemarkar, AWS Sr. Partner Solutions Architect, discuss practical ways to mature your MLOps approach including bringing model use and development into your existing secure software supply chain and development processes. Watch to learn more and get a demo of the JFrog and Amazon SageMaker integration.

Keeping humans in the loop of AI-enhanced workflow automation: 4 best practices

In today's rapidly advancing technology landscape, the role of people in workflow automation and orchestration is more critical than ever. At Tines, we firmly believe that human oversight should be an integral part of important workflows, ensuring that all decisions are grounded in context and experience. AI in Tines is secure and private by design. This means the platform doesn’t train, log, inspect, or store any data that goes into or comes out of language models.

TracFone Breach Underscores Critical Need for Mobile Carrier API Security

The recent Federal Communications Commission (FCC) settlement with TracFone Wireless, Inc. (TracFone) for $16 million highlights a critical vulnerability within the mobile telecommunications industry: API security. The investigation revealed unauthorized access to customer data through weaknesses in TracFone's mobile carrier APIs. This incident reminds mobile carriers to prioritize robust API security measures to safeguard customer data and ensure network integrity.

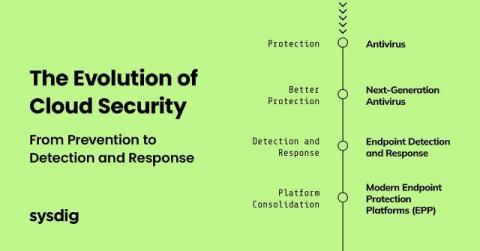
The evolution of cloud security: Lessons from the past to navigate the future

Remember asking your teachers when you would need to know history facts outside of school? They probably said that learning history is important in understanding our past and how society has changed and progressed over time, and that we can learn from past experiences and mistakes. They were right, of course (even if it might not have felt like it then). And that’s all equally true when it comes to the history of security.