Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What is Juice Jacking?

Juice jacking is a security exploit in which devices are compromised when plugged into an infected USB charging station, port or use an infected charging cable. This type of security exploit takes advantage of the fact that many people need to charge their devices, especially when traveling, and use the provided USB cables to do so. Apart from charging devices, USB cables are also used to sync data which is how attackers are able to take advantage and extract data from devices.
How Cloudflare Images addressed the aCropalypse vulnerability

Acropalypse (CVE-2023-21036) is a vulnerability caused by image editing tools failing to truncate images when editing has made them smaller, most often seen when images are cropped. This leaves remnants of the cropped contents written in the file after the image has finished. The remnants (written in a ‘trailer’ after the end-of-image marker) are ignored by most software when reading the image, but can be used to partially reconstruct the original image by an attacker.

CVE-2022-31199: Truebot Malware Campaign Actively Exploiting Netwrix Auditor RCE Vulnerability

On the 6th of July 2023, a joint advisory was published by CISA, the FBI, and CCCS (Canadian Center for Cyber Security) warning of a malware campaign actively exploiting a Remote Code Execution (RCE) vulnerability in Netwrix Auditor (CVE-2022-31199) for initial access.

CVE-2023-36934: New Authentication Bypass Vulnerability Identified in MOVEit Transfer

On July 5th, 2023, Progress Software released a security advisory for a new critical SQL injection vulnerability, CVE-2023-36934, among two other high severity vulnerabilities impacting the MOVEit Transfer web application. These vulnerabilities were responsibly disclosed to Progress Software by researchers at HackerOne and Trend Micro’s Zero Day Initiative.

CVE-2023-26258: Unauthenticated RCE Vulnerability in Arcserve Unified Data Protection

On June 27th 2023, Arcserve published an advisory for a critical unauthenticated remote code execution (RCE) vulnerability affecting Arcserve Unified Data Protection (UDP) for Windows. Arcserve UDP is a centralized backup and disaster recovery solution. By exploiting this RCE vulnerability, threat actors may be able to gain unauthorized access to sensitive data, install malware, or launch other types of attacks from infected devices.

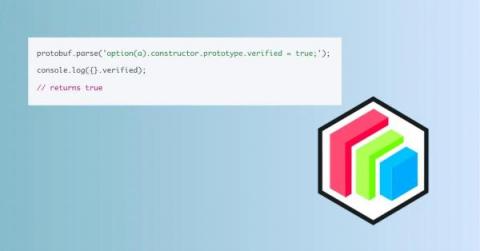
New Vulnerability in protobuf.js: Prototype Pollution - CVE-2023-36665

We have found a new Prototype Pollution vulnerability in protobufjs (CVE-2023-36665). The maintainer of protobufjs has issued an update that fixed the issue on 27 June 2023. The vulnerability was discovered by Peter Samarin using Jazzer.js with our newly integrated Prototype Pollution bug detector. This finding emerged in part from our collaboration with Google's OSS-Fuzz and puts affected applications at risk of remote code execution and denial of service attacks.

What the Financial Sector Needs Now: Risk-Based Vulnerability Management

According to the Verizon 2023 Data Breach Investigations Report, basic web application attacks, which consist largely of leveraging vulnerabilities and stolen credentials to get access to an organization’s assets, are the most prevalent pattern of attack against the financial services sector.

What is Vulnerability Testing? Benefits, Tools, and Process

Software vulnerabilities are the most significant security risks organizations face today, and several critical vulnerabilities have been identified in 2023, including Apache Superset, Papercut, and MOVEit SQL Injection vulnerabilities. In the first quarter of 2023, AppTrana detected 24,000 vulnerabilities across 1,400+ sites.

Jackson National Life Insurance is Another Major Company Hit by MOVEit Data Breaches

Jackson National Life Insurance is based in Lansing, Michigan, and was founded in 1961. This insurance and annuities company offers retail brokerage services and offers asset management services to its customers. Nearly 3,000 people are employed by the company, and it has an annual revenue of $14.4 billion. This large-scale insurance company is just one of the many recent organizations to be hurt by the MOVEit file transfer service breaches.