Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI Helped Find Critical PHP Flaws: 4 Things to Do Today

AI helped researchers find two critical PHP flaws, and one sat in the code for at least a decade. PHP runs roughly 70% of websites, and attackers were probing on the day the patches shipped, October 21. Dirk Schrader, VP of Security Research at Netwrix, lists four things to do today: update to PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35 and restart the workers; on PHP 8.1 or older, where there’s no official release, use vendor extended support or take the server offline; check your logs and web roots from before the patch; and limit the account PHP runs under.

Critical vulnerability: OpenSSH authentication bypass on Alpine Linux (CVE-2026-123158)

On November 5, 2026, Alpine Linux published a security advisory for an authentication bypass in its openssh-server package, nicknamed sshole by researcher Özgün Kültekin of Wakefield, who reported it. An attacker who can reach the SSH port can log in to accounts that have no password set, such as key-only users, without knowing any password. Every Alpine release from 3.16 through 3.24 and edge is affected. No CVE identifier has been assigned yet. Fixed packages are available.

Black October? What PHP2Shell Tells Us About the Future of Vulnerabilities

October was a busy month for AI and security, with the story that got the most attention being PHP2Shell. On 20th October the PHP security team announced an out-of-cycle release for two critical remote code execution flaws in the PHP interpreter (CVE-2026-109618 and CVE-2026-109619), affecting every version of PHP, from 5.4 through 8.5.

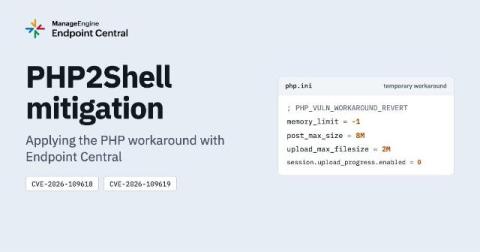
PHP2Shell mitigation: Applying the PHP workaround with Endpoint Central

On October 21, 2026, PHP fixed two critical unauthenticated remote code execution flaws, CVE-2026-109618 and CVE-2026-109619. CISA added both to its Known Exploited Vulnerabilities catalog on October 26th. The real fix is upgrading PHP and restarting every worker process. But many Windows servers can’t do that yet: the vendor hasn’t certified the new version, the PHP branch is end-of-life, or nobody knows whether a PHP copy exists inside an old application.

Snyk Named a Leader in The Forrester Wave: Agentic Development Security Tools, Q4 2026

We're proud to share that Snyk has been named a Leader in The Forrester Wave: Agentic Development Security Tools, Q4 2026. Snyk received the highest score in the Strategy category, along with the highest scores possible in these criteria.

A Prioritized Backlog Is Still a Backlog

Vulnerability prioritization helps security teams identify what matters most, but it doesn’t actually resolve exposures. Even with better visibility, deduplication, and risk-based context, vulnerabilities remain unresolved until teams investigate, remediate, and verify the fixes. Real risk reduction isn’t about how efficiently you organize your backlog. It’s about how quickly you take action to shrink it.

Introducing Zero Wire, a hub for investigating critical Internet vulnerabilities

You run security at your organization. It’s 7:00 am, and you’re having breakfast. You receive a ping: a new critical vulnerability has been disclosed. Your team scrambles to compare vendor advisories, read technical research, check which systems run the affected software, and answer familiar questions from the business: are we affected, and what are we doing about it? Another disclosure arrives before that work is finished.

From Directive to Deadline: Operating BOD 26-04 in the Real World

BOD 26-04 changes how federal agencies and FedRAMP providers handle vulnerabilities. It moves away from severity-based, 30-day patching and toward risk-based prioritization. In this webinar, Bob Costello (former CIO of CISA, strategic advisor to Nucleus Security, and Chief Digital and Information Officer at The Merlin Group) and Scott Kuffer (Co-founder and CPO at Nucleus Security) explain what the directive requires, why CISA built it on the SSVC decision-tree framework, and how to put it into practice.