Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Fixing half a million security vulnerabilities

Hackathons are well known among software development teams for driving innovation and collaboration. So, what if we applied that model to cybersecurity to improve an organization’s application security posture? That would be a dream come true for any CISO and security practitioner — and is exactly what we set out to do at Snyk in February 2023. Check out some of the funniest moments from our panels.
Snyk in a galaxy far away

In honor of May the 4th, we’re featuring a narrative from an Imperial trooper in a faraway galaxy as he reflects on his organization’s worst day and how it could’ve gone differently. Don’t get me wrong. I’m still proud to work for one of the most formidable organizations in the galaxy. But as most of you probably know, we’ve recently hit quite a setback. Our higher-ups decided to build a space station.

Run Faster, Runtime Followers

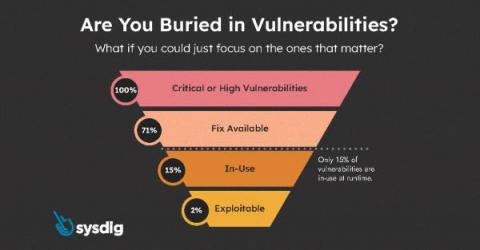
Recently, there has been a flurry of announcements claiming to have what we call Runtime Insights, the ability to prioritize vulnerabilities. Here are two examples: I can confirm that this approach works, and it works very well. It substantially decreases the number of vulnerabilities that a team has to manage, sometimes by a factor of 100 or more! How do I know it? Because Sysdig invented this approach.

Zero day remediation tips: Preparing for the next vulnerability

Businesses increasingly run on software, which, unbeknownst to its developers, can contain vulnerabilities that attackers often discover and exploit before a patch is available. This makes zero day attacks inevitable, but you can reduce their impact in your network and across your supply chain if you’re prepared to act fast.

A Mere Five Percent of Vulnerable Enterprises Fix Their Issues Every Month: How to Help Them Do Better?

Software vulnerabilities are one of the leading threats to an organization's cybersecurity posture, yet recent research from Bitsight reveals that enterprises affected by software vulnerabilities resolve them at a typical compound rate1 of only about 5% per month compounded continuously. However, there is evidence of much faster remediation for certain classes of vulnerabilities.

CVE-2023-21932: Critical Unauthenticated RCE Vulnerability in Oracle Hospitality OPERA 5 Property Services

Oracle recently released their Critical Patch Update addressing 433 vulnerabilities across their products, including a vulnerability in the Oracle Hospitality OPERA 5 Property Services product. According to Oracle’s vulnerability description, CVE-2023-21932 is a difficult– to– exploit vulnerability, requiring network access via HTTP and high privileges.

Security implications of HTTP response headers

When a web server receives an HTTP request, it is processed and sent back with a response containing the requested resource and any additional information in the form of HTTP response headers. These headers provide important data, such as last-modified dates, content types, and cache-control settings. The browser then uses this information to determine how to display or store that particular resource. This process helps ensure efficient communication between web servers and browsers.

Can AI write secure code?

AI is advancing at a stunning rate, with new tools and use cases are being discovered and announced every week, from writing poems all the way through to securing networks. Researchers aren’t completely sure what new AI models such as GPT-4 are capable of, which has led some big names such as Elon Musk and Steve Wozniak, alongside AI researchers, to call for a halt on training more powerful models for 6 months so focus can shift to developing safety protocols and regulations.

API3:2019 Excessive Data Exposure: Understanding the Risks, Impacts, and How to Prevent It

Excessive data exposure occurs when APIs reveal more fields, data, and information than the client requires through the API response. Excessive data exposure flaws expose all object properties to API calls rather than what the user needs to act on without considering the object’s sensitivity level. This vulnerability exposes you to data leaks, man-in-the-middle attacks, and other cyber threats. That is why excessive data exposure in APIs is listed as #3 in the OWASP API Security Top 10 2019.