Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Exposure as a Competency: How Agentic Exposure Management Can Differentiate High-Performing Teams

In today's fast-paced work environment, the factors that distinguish high-performing teams go well beyond technical skills and traditional leadership. Increasingly, organizations are recognizing "exposure" as a critical competency, one that shapes how teams interact with uncertainty, opportunity, and risk. While exposure has historically been viewed through a financial or risk management lens, it is now emerging as a core driver of organizational agility, innovation, and resilience.
Trusted AI Video Platforms for Safer Content Creation

AI-generated video content is growing fast, and so are the risks that come with it. Statista data shows a sharp rise in AI incidents tied to content generation, with deepfakes and rights violations among the most documented concerns. For creators, brands, and marketers, choosing the right AI video platform means thinking beyond output quality.

Top AI cybersecurity companies in 2026

AI cybersecurity companies in 2026 fall into two categories: platforms using AI to automate detection, investigation, and response, and platforms built to secure the AI systems organizations are now deploying. With this grouping into ‘AI for Security’ and ‘Security for AI’, this article covers the breadth and depth of AI cyber security companies.

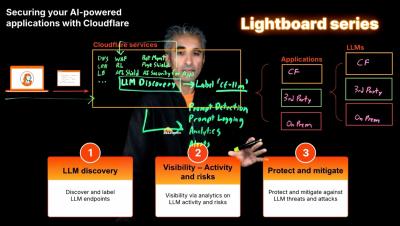
Lightboard series - Secure your AI-powered applications with Cloudflare

Humair from Cloudflare walks through the details of how Cloudflare's AI Security for Apps secures AI-powered applications. Learn how Cloudflare can discover AI/LLM endpoints and detect and mitigate AI-specific threats like PII exposure, unsafe/toxic content, prompt injection and jailbreak. Learn more.

Every Tech Revolution Follows This Pattern (AI Is No Different)

AI adoption is happening faster than any technology cycle in history. Information security and risk management are being sacrificed for speed and every single technology revolution has followed the same pattern. In this episode of Razorwire Raw, Jim Rees draws on decades of experience through the internet boom, virtualisation revolution and cloud computing adoption to explain what's actually happening with AI right now. Each cycle has been faster than the last, and each time, security gets left behind.

What is the OWASP Top 10 for LLM Application Security

Initially published by the Open Worldwide Application Security Project (OWASP) in 2023, the Top 10 for LLM Application Security list seeks to bridge the gap between traditional application security and the unique threats related to large language models (LLMs). Even where the vulnerabilities listed have the same names, the Top 10 for LLM Application Security focuses on how threat actors can exploit LLMs in new ways and potential remediation strategies that developers can implement.

AI Workload Baseline and Drift Detection: Defining "Normal" Agent Behavior

Security teams deploying AI agents into Kubernetes know they need behavioral baselines. The concept is straightforward: define what “normal” looks like for each agent, then detect when behavior drifts in ways that suggest compromise. The problem is that AI agents are designed to change. A model update alters inference latency. A prompt revision shifts tool-calling sequences. A new MCP integration adds API destinations nobody flagged during the last security review.

How to Triage an AI Agent Execution Graph: A Three-Tier Decision Framework for Security Teams

A platform security engineer gets an alert at 2:14 a.m. One of the LangChain agents running in their production Kubernetes cluster has produced an execution graph with eleven nodes, seven tool calls, and an egress edge to a domain that is not in the agent’s approved integration list. The chain is fully rendered in their console. Every signal is there.

The CISO's AI Agent Production Approval Checklist: 7 Gates to Clear Before Go-Live

Your engineering lead is in your office Thursday morning. They want to push an AI agent to production next Tuesday. It’s a LangChain-based workflow agent, connected through MCP to three internal tools and one external API, with access to a customer database. The framework posters are on the wall. Your team has spent two quarters standing up runtime observability. And sitting in that chair, you still don’t know whether to say yes.