Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Era of Agentic Security is Here: Key Findings from the 1H 2026 State of AI and API Security Report

The era of human-centric API consumption is officially ending. Over the past year, enterprises have rapidly transitioned from simply experimenting with Generative AI to deploying autonomous AI agents that drive core business operations. These agents act as digital employees. They utilize Large Language Models (LLMs) for reasoning, Model Context Protocol (MCP) servers for connectivity, and internal APIs for execution. This evolution has fundamentally altered the enterprise attack surface.
Secret Scanning For AI Coding Tools With ggshield

Introducing ggshield AI hooks from GitGuardian to help stop AI coding assistants from leaking secrets. See how ggshield can scan prompts, tool calls, file reads, MCP calls, and tool output inside AI coding tools like Cursor, Claude Code, and VS Code with GitHub Copilot. When a secret is detected, ggshield can block the action before sensitive data is sent or exposed. You will also see how simple the setup is, with flexible install options for local or global use. This adds practical guardrails to AI-assisted development and helps teams move fast without increasing secret sprawl.

Enterprise AI Security Use Cases: What Security Teams Are Solving For

Enterprise AI adoption is no longer a future problem. The average organization uses 54 generative AI (genAI) applications, and endpoint AI agent adoption is accelerating, with Cyberhaven research tracking 276% growth in 2025. Security programs have struggled to keep pace with either trend. The AI security gap is technical, not philosophical. Most organizations have AI acceptable use policies.

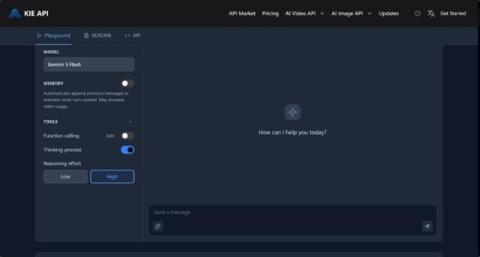
Building Smarter Virtual Assistants with Gemini 3 Flash API: AI for Seamless Workflow Automation

As teams become more distributed and workloads continue to increase, the need for effective automation tools has never been greater. Traditional methods of collaboration often fall short when it comes to handling repetitive tasks, managing high volumes of information, or providing real-time, intelligent support. That's where AI virtual assistants come in, changing how teams collaborate, streamline workflows, and boost productivity.

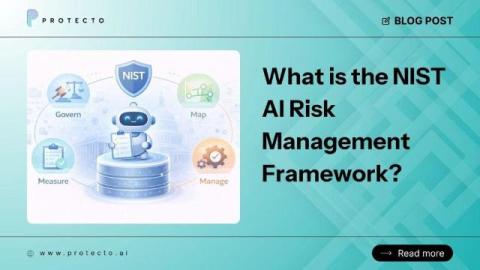
What is the NIST AI Risk Management Framework?

The NIST AI Risk Management Framework is a guide that helps organizations spot and reduce risks in AI systems. This framework was released in January 2023 by the U.S. National Institute of Standards and Technology. The framework is built around four key steps, namely: Govern, Map, Measure, and Manage, and is meant to help teams responsibly use AI. It doesn’t matter which industry you work in or which AI you use; this framework works everywhere.

How Weak AI Governance Is Creating A Security Disaster #cybersecurity #aisecurity

This episode explores why CTEM matters in a world of vibe coding, AI agents and rapidly expanding attack surfaces. It covers prompt injection, hidden threats, deepfakes, weak governance and the growing fear that businesses are deploying AI far faster than security teams can understand or control it.

Exploring CSPM: What is Cloud Security Posture Management?

Cloud Security Posture Management (CSPM) is a category of cloud security tooling that automates the identification and remediation of misconfigurations and security risks across cloud environments. CSPM solutions continuously monitor how cloud resources are set up, compare those configurations against industry benchmarks and organizational policies, and flag issues that could create security exposure.

The Agentic Identity Crisis: Why Your AI Agents Are Your Biggest Identity Blind Spot in 2026

An intern gets admin access to production for a temporary task, but nobody remembers to revoke it. Imagine that intern works at machine speed, never sleeps, and can chain dozens of actions before you’ve read the Slack ping—and has no instinct for when they’re about to do something irreversible.