Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

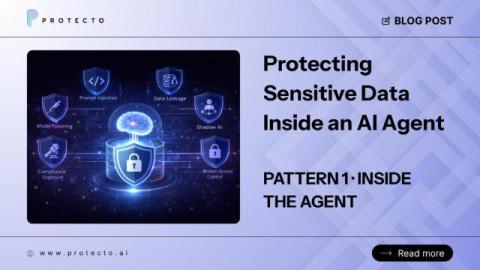
AI Security Has a Context Problem

The problem is not a lack of controls. It is connecting them into one attack story. The more time I spend with enterprise AI deployments, the clearer one thing becomes: AI security is incredibly fragmented. There are LLM guardrails, AI gateways, MCP security tools, API security, endpoint controls, SASE, code scanning, and runtime detection. Each solves a real problem, but agentic systems do not experience them as separate layers, and neither do attackers.

The AI-powered GRC team: Scaling compliance, not complexity

GRC teams have invested heavily in building mature control frameworks. But the real challenge? Having the visibility into whether they’re working, where gaps exist, and how to keep them running effectively at scale. As compliance programs become more complex, teams need new ways to move beyond manual processes and maintain confidence in control effectiveness. Join GRC experts from Tines for a conversation with Ayoub Fandi, Founder of GRC Engineer, to learn how leading organizations are reducing manual effort and improving visibility, and building compliance programs that scale.

How to Make Smart Security Decisions in the AI Era

AI is changing the speed and scale of cyber risk, but the fundamentals of security remain the same. Elisa Costante, VP of Software Engineering at Forescout, discusses why visibility, risk assessment, and adaptive controls are essential for protecting organizations against rapidly evolving threats. Learn more.

AI Governance in healthcare: Compliance and security

AI governance in healthcare has become a question boards and auditors ask directly. They want to know which AI tools reach protected health information, who's accountable for each one, and what evidence shows the controls are holding. Most health systems have a written policy and no way to produce those three answers on request, which is precisely what an auditor tests. Healthcare organizations adopted AI faster than they built the governance to account for it.

Session on Air-Gapped AI: Architecture, Challenges and Best Practices at GISEC Global 2026

In this Session at GISEC Global 2026, Dubai Exhibition Centre (DEC), Expo City, our Founder & CEO, Mr. Anirban Mukherji, discussed the importance of balancing AI innovation, data sovereignty, privacy, and national security in the era of frontier Large Language Models.

The New Agent Control Standard Names the Controls, Not Their Value

The OWASP GenAI Security Project unveiled an Agent Control Standard in early September, donated to the project and aimed at runtime enforcement for agentic systems. It sets out that agents should be inspectable, traceable and instrumentable, with declarative hooks and policy enforcement across frameworks. ‍ It answers which controls belong around an agent.

How Early Action Helps Organizations Stay Ahead

In a rapidly changing technology landscape, waiting for consensus can mean losing the advantage. Elisa Costante, VP of Software Engineering at Forescout, explains how acting early helps organizations build understanding, adapt to change, and stay ahead as AI transforms cybersecurity for defenders and attackers alike.