Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

CMMC readiness: How AI-powered platforms accelerate DoD compliance

Defense contractors and organizations involved in Department of Defense (DoD) projects are facing growing pressure to comply with stringent cybersecurity standards. The Cybersecurity Maturity Model Certification (CMMC) represents a transformative initiative aimed at enhancing the security posture across the defense industrial base. As organizations embark on this compliance journey, AI-powered platforms are emerging as critical enablers to accelerate CMMC readiness.
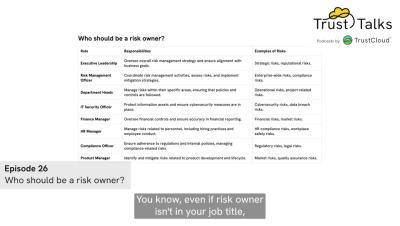
Who should be a risk owner? | TrustTalks - Ep 26 | Security and GRC Podcast

This podcast focuses on the roles and responsibilities of risk owners within an organisation’s risk management framework. It outlines key responsibilities, required skills and qualifications for effective risk ownership, and provides examples of who might fill this role (e.g., executive leadership, department heads).

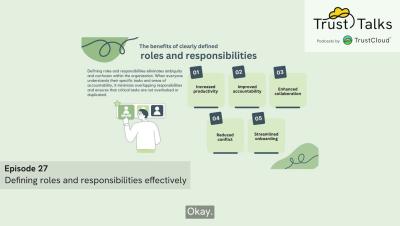
Defining roles and responsibilities effectively | TrustTalks - Ep 27 | Security and GRC Podcast

This podcast focuses on the importance of clearly defined roles and responsibilities for enhanced organisational efficiency, accountability, and collaboration, offering practical steps and tools for implementation. It showcases TrustCloud resources, including training materials, forums, and a GRC Launchpad offering numerous guides on governance, risk, and compliance (GRC), security, and privacy topics focusing on improving organisational effectiveness through better structure and understanding of GRC principles.

SOC 2 Compliance for SaaS Companies

Is your SaaS company struggling to close those big enterprise deals? Chances are, they're asking for SOC 2 compliance – and for good reason! A staggering 82% of enterprises demand SOC 2 compliance from their SaaS vendors to mitigate data breach risks (Cloud Security Alliance, 2023). Without it, you're missing out on massive opportunities!

ISO 27001 beyond IT: Building a culture of security across the enterprise

The digital era has spurred organizations to rethink how they protect sensitive data, necessitating a robust and holistic approach to security. Although ISO 27001 is widely recognized as a framework for managing IT security, forward-thinking leaders are discovering that its principles can be extended far beyond IT departments.

Transform the audit experience with Vanta

Audit firms today face pressure to deliver faster, more accurate audits while meeting rising client expectations. Clients often operate with complex tech stacks, outdated evidence-gathering workflows, multiple frameworks, and numerous workspaces—all of which auditors must manage alongside their own established tools and processes.

The Rising Demand for Software Architecture Consulting Services in Finance and Healthcare

Today's financial and healthcare sectors are experiencing a dramatic transformation. Digital innovations, data volumes, and cyber threats contribute to an increasingly complex landscape. This is where software architecture consulting services come into play - helping organizations create resilient, adaptable, and compliant software systems.

Best Practices to Tackle Cybersecurity Challenges in Custom Enterprise Software

Businesses heavily rely on custom enterprise software to handle tasks like customer relationships, finance and accounting, or data analytics. Enterprise solutions from reliable developers like GP Solutions offer some much-needed flexibility. The catch is that they can introduce unique security risks, such as unvetted custom code, misconfigurations, and weak or inconsistent security controls. Here's the good news: Enterprises can avoid these challenges early on if they understand the proper security measures to implement.

Unlocking time and budget for teams with security automation

As security threats become increasingly sophisticated and the landscape of cyber attacks evolves, organizations are compelled to reexamine their investments and strategies in cybersecurity. One critical lever for improving security effectiveness and efficiency is automation. When implemented correctly, automation enables security teams to unlock significant time and budget savings, making them more agile, resilient, and proactive in combating threats while reducing the burden of routine tasks.