Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

A Guide to ISO 27001 Clauses - Updated for 2026

Around the world, nearly 100,000 businesses have navigated the challenges of ISO 27001 and earned their certifications. If you want your business to be the next on the list, you need to understand the 11 clauses that make up the security framework, including what they are, why they exist, and what they require you to do. Let's start where you might reasonably expect to begin: with a definition of what the clauses are.

Securing Commercial Properties After Severe Storm Damage

When a severe storm hits a commercial facility, the aftermath can be catastrophic. High winds, torrential rain, and flying debris disrupt daily operations and threaten structural stability. Property managers face immediate pressure to protect the assets and minimize financial losses. Taking immediate control of the situation prevents minor issues from turning into major disasters. Speed matters when dealing with natural elements that continue to damage a building long after the clouds clear. A proactive response limits operational downtime.

Dedicated Server Hosting: Benefits, Use Cases and Pricing in 2026

Despite the rapid growth of cloud platforms, the dedicated server market continues to expand. Many companies still choose dedicated server hosting for hosting corporate applications, databases, SaaS platforms, high-traffic web services, and artificial intelligence infrastructure. The reason is simple. Not every workload can be efficiently handled in a virtualized environment. Many projects require guaranteed computing resources, consistent performance, full server control, and the ability to customize hardware according to specific business requirements.

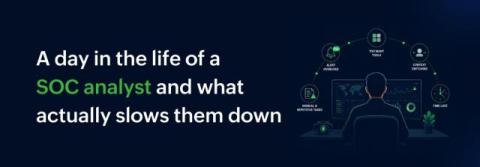
A day in the life of a SOC analyst-and what actually slows them down

In the current threat landscape, the pressure on security operations center (SOC) teams has never been higher. Yet for many organizations, the reality of daily security operations is less high-tech threat hunting and more of an uphill battle against manual processes and fragmented data. To understand why SOC teams are burning out, let's walk through a typical morning of an SOC analyst.

What Is an RFP Response? A Guide for Security and GRC Teams

A request for proposal (RFP) response is a vendor's formal reply to a procurement document where a prospective buyer outlines all the information they need to make a final purchasing decision. It acts as a detailed pitch, typically covering pricing, solution architecture, references, and implementation timelines. For security and governance, risk, and compliance (GRC) teams, the section that consistently creates the most friction is the security and compliance questionnaire embedded inside an RFP.

Frontier Model Is the Wrong Meter for Continuous Security

The economics of continuous security at frontier-model prices, and why the math points back to independence. The frontier models are astonishing at finding vulnerabilities. That is not in dispute, and it is not what this piece is about. The question is not whether a frontier model can find a flaw in your code. It is whether you can afford to run one as your scanner, continuously, across your entire estate, the way real security actually works.