Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI SOC Metrics That Actually Matter: How to Measure Whether AI Is Working in Your SOC

Every security vendor shipping an AI product in 2026 makes the same promises. Faster triage. Shorter response times. Fewer false positives. Reclaimed analyst hours. But, six months after deployment, most security leaders still cannot answer a straightforward question from the board: Is this thing actually working?

Cato CTRL Threat Research: New Vulnerabilities in NVIDIA NeMo and Meta PyTorch Enable Full System Compromise

Cato CTRL has discovered high-severity vulnerabilities in NVIDIA NeMo (CVE-2025-33236 with a CVSS score of 7.8) and Meta PyTorch that turns AI model files into remote code execution (RCE) vectors. The NeMo vulnerability allows RCE by importing a malicious AI model. The NeMo framework silently executes threat actor-controlled code with no warning.

10 top ITDR tools for identity-centric security in 2026

Identity threat detection and response (ITDR) tools close the visibility gap that EDR and MFA leave open. They surface credential misuse, lateral movement, and Active Directory activity that appears legitimate to endpoint and perimeter defenses. The right fit depends on your identity infrastructure, detection depth, and whether you need real-time blocking or post-event response.

What is Security Debt and What Should Your Organization Do About it?

Businesses are constantly investing in new security tools to protect their digital environments. However, many organizations are only tapping into a small fraction of what those tools can actually do. This massive amount of unused potential adds up to something called security debt: a growing risk for organizations of all sizes. Security debt occurs when tools capable of mitigating threats are underutilized, misconfigured, or left idle.

Top Tools Used to Bypass Cloudflare for Web Scraping: A Security Perspective

Cloudflare protects more than 20% of all websites on the internet, according to W3Techs infrastructure data. Its layered security model combines IP reputation filtering, TLS fingerprinting, JavaScript challenges and behavioural analysis to block automated traffic before it reaches the origin server.

How Cyber Resilience Supports Long-Term Security Goals

In recent years, cyber resilience has moved from being an option to a huge necessity. With organizations becoming a constant target for digital threats, the need for protection, prevention, and deterrence strategies has become more pertinent than ever. Resilience is about being prepared for disruptions, responding quickly, and recovering thoroughly. This makes it easy to secure information and builds faith in the long run.

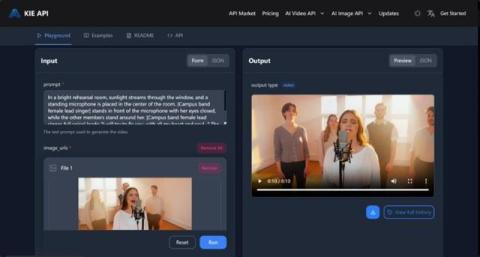
Kling Video 2.6 API: How to Build Automated Visual Simulation Workflows

The landscape of generative media has shifted from simple prompt-based experimentation to sophisticated, integrated production pipelines. With the release of Kling 2.6, the focus has moved toward "Native Audio-Visual Generation"-a breakthrough that allows developers to synchronize high-fidelity visuals with context-aware sound in a single automated step. For platforms focusing on digital senses and technical security, the Kling Video 2.6 API offers a robust framework for building simulations that were previously too resource-intensive to automate.

Why you need Active Roles, even if you have IGA

Here are three scenarios I come across frequently with customers of all sizes, in all industries, when discussing Active Roles by One Identity: These situations come from customers on all points of the "identity security maturity" spectrum. Those who have nothing in place or some things in place or an entire stack of fully implemented solutions in every category.

Step-by-Step: How to Set Up a Homelab for Penetration Testing at Home

Cybersecurity is more important than ever. One of the key components of cybersecurity is penetration testing, which involves intentionally attempting to exploit a system to identify vulnerabilities. It is commonly known as ‘ethical hacking’. Penetration testing, or pen testing, requires strong hands-on skills. Setting up a homelab is an effective way to gain practical experience in a safe, controlled environment.

Best SAST Tools in 2026: Top 10 Solutions Reviewed

SAST (Static Application Security Testing) tools analyze an application’s source code to identify potential security vulnerabilities without executing the code. They are crucial for finding security flaws early in the development lifecycle, helping developers address issues before they become more costly and difficult to fix. This guide covers the best SAST tools available in 2026 and how to evaluate them.