Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Bitdeer Extends Its Infrastructure Strategy From Bitcoin Mining to Full-Stack AI Cloud and Model Studio

Every mining cycle returns to the same unromantic question: what does one megawatt earn after the electricity bill? As hashprice narrows the margin on mining hardware, AI workloads offer power-rich operators another source of revenue. Bitdeer's move into full-stack AI Cloud is therefore less a change of identity than a change in how infrastructure gets paid.
List of Best VMware Alternatives in the UAE

If you're a CIO in the UAE, you've probably had at least one conversation this year about what happens after VMware. Broadcom's licensing changes shook up a lot of long-term customers, and plenty of IT teams here are quietly running the numbers on what a move would cost. The good news is you're not short on options. The tricky part is that "VMware alternatives" in the UAE cover two different paths, and mixing them up leads to messy decisions.

How to secure Exchange Server beyond the CVE-2026-62911 fix

Remote access has always been a core part of how on-premises Exchange works. Users need OWA to read their email from outside the office. Their devices need Autodiscover to set themselves up automatically. Keeping both reachable means keeping Exchange accessible from the Internet, and that opens up more of the server than most organisations realise. CVE-2026-62911 is the latest example. Microsoft released the fix on August 11, 2026.

Top 9 Netwrix Auditor reports for NIS2 compliance audits

NIS2 changes what "good enough" security looks like for a huge slice of the European economy. If your organization operates in energy, transport, finance, health, digital infrastructure, or any of the other sectors the directive designates as critical infrastructure, you can no longer choose whether to formalize your cybersecurity risk management. Instead, you have to decide how fast you can prove it.

How to Mark and Label CUI Correctly for CMMC

CMMC is vast and complex, but when you drill down to the heart of it, it's all about one thing: properly securing CUI. And yet that, in and of itself, is a problem. All CUI needs to be marked, which means if you receive CUI from your agency or prime, it needs to be properly marked. And it means if you produce CUI, you need to mark it properly yourself. How do you know what is and isn't CUI, and how do you mark it properly? What happens if you get it wrong?

Stopping Data Exfiltration From Departing Employees

Departing employees still email files to personal accounts and copy them to USB drives. Now they also paste sensitive content into ChatGPT, Claude, or Gemini to summarize a codebase, draft a portfolio piece, or package a project before their last day. Neither channel has replaced the other. The attack surface has simply gotten wider, and most security teams are still staffed and tooled for the channels they already know how to watch.

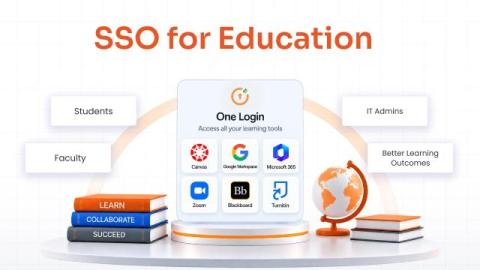
SSO for Education: Secure and Simplify Access to Learning Applications

Students, teachers, and faculty now move across a growing stack of learning, collaboration, communication, and administrative applications. Every new platform can mean another login to remember and another account for IT teams to manage. That creates friction for users and a growing access-management burden for institutions. SSO for education brings these applications behind a central authentication layer, allowing users to access authorized services with one institutional identity.

Cloud Infrastructure Entitlement Management (CIEM): A Complete Guide

In the cloud, an identity is no longer necessarily a person. It can be an application calling an API, a workload accessing storage, a service account running an automated process, or a machine interacting with another cloud resource. Each needs permissions to operate, and each becomes part of an access environment that changes as quickly as the infrastructure itself. This has expanded identity security beyond managing users and accounts to governing a much larger ecosystem of human and non-human access.

The Cyber Loss That Fits Inside a Single Weekend

An annual exposure figure for a retailer treats the year as uniform. Divide expected loss across twelve months, apply a duration, produce a number. The instinct that this understates a peak-season outage is correct and the usual reason given for it is wrong. ‍ The concentration is not where people assume, and the mechanism that makes a December outage expensive is not volume. It is that the demand has a deadline. ‍

The AI Agent Whose Builder Already Left

Somebody in operations builds an automation inside a sanctioned platform to solve a problem in their own workflow. It works, other people come to depend on its output, and eighteen months later that person leaves. ‍ The platform still lists the automation. Nobody inherits it, because it was never anybody's asset to begin with, and the offboarding checklist has no line for a thing that was never recorded as belonging to the person departing. ‍