Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

List of Best VMware Alternatives in the UAE

If you're a CIO in the UAE, you've probably had at least one conversation this year about what happens after VMware. Broadcom's licensing changes shook up a lot of long-term customers, and plenty of IT teams here are quietly running the numbers on what a move would cost. The good news is you're not short on options. The tricky part is that "VMware alternatives" in the UAE cover two different paths, and mixing them up leads to messy decisions.
How to secure Exchange Server beyond the CVE-2026-62911 fix

Remote access has always been a core part of how on-premises Exchange works. Users need OWA to read their email from outside the office. Their devices need Autodiscover to set themselves up automatically. Keeping both reachable means keeping Exchange accessible from the Internet, and that opens up more of the server than most organisations realise. CVE-2026-62911 is the latest example. Microsoft released the fix on August 11, 2026.

The Cyber Loss That Fits Inside a Single Weekend

An annual exposure figure for a retailer treats the year as uniform. Divide expected loss across twelve months, apply a duration, produce a number. The instinct that this understates a peak-season outage is correct and the usual reason given for it is wrong. ‍ The concentration is not where people assume, and the mechanism that makes a December outage expensive is not volume. It is that the demand has a deadline. ‍

The AI Agent Whose Builder Already Left

Somebody in operations builds an automation inside a sanctioned platform to solve a problem in their own workflow. It works, other people come to depend on its output, and eighteen months later that person leaves. ‍ The platform still lists the automation. Nobody inherits it, because it was never anybody's asset to begin with, and the offboarding checklist has no line for a thing that was never recorded as belonging to the person departing. ‍

What is ISMS-P and how it aligns with ISO 27001 and ISO 27701

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

What PCI DSS 4.0 Requires for Infrastructure Identity and Access Evidence

Most conversations about PCI DSS 4.0 start with the requirements, but I’d rather start with a habit. As a GRC & Cybersecurity Consultant advising organizations preparing for PCI DSS 4.0 assessments, I’ve developed a habit of observing how findings move from identification to ownership, remediation, and documented closure. That’s often where accountability gaps and unresolved findings surface first.

How To Eliminate Secrets Configuration Drift Between Your Vault and the Cloud

You might treat a centralized vault as the authoritative source for every secret, but secrets can quietly fall out of sync as they get copied into cloud secret stores, CI/CD pipelines and running workloads. This is referred to as secrets configuration drift, and it can leave outdated or standing credentials, API keys and other secrets active for longer than intended.

Recognizing and detecting data exfiltration

Every breach that lands a CISO in front of the board has a common final act: Data leaving the building. Attackers don't get paid for breaking in. They get paid for what they take out. And by the time stolen data appears on an extortion site or in a regulator's inbox, the window to stop the damage has already closed. That is what makes exfiltration so dangerous. It rarely looks like an emergency.

OT: The Other Technology Evolution

Written by Bill Moore, CEO & Founder TL;DR In Part 1 of this series, I looked at how computing and telecommunications gradually became what we now call Enterprise IT. That change did not happen because someone decided to merge two departments. It happened because the technologies, the systems, and the work they supported became too interconnected to describe separately.

Enforce custom rules in Datadog IaC Security scanning

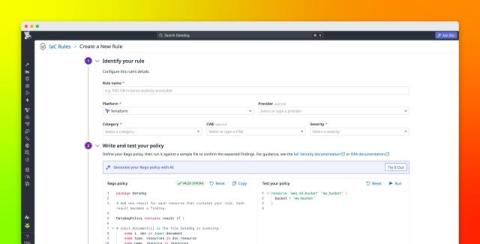
Infrastructure-as-code (IaC) security scanning can catch common misconfigurations before deployment, but every organization also has internal requirements that a default rule catalog cannot cover. For example, teams may need to enforce required tags, approved instance types, or naming conventions. With custom rules for Datadog IaC Security, security and platform teams can define these requirements as Rego policies and run them alongside Datadog’s default rules during IaC scans.