Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

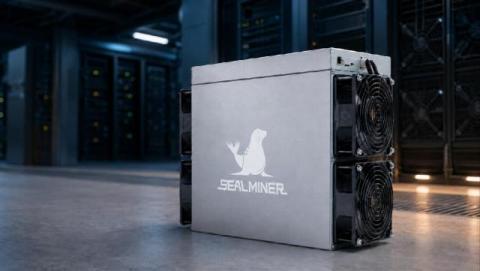
Global Bitcoin ASIC Miner Benchmark 2026: Comparing Efficiency and Rack Density Across Leading Models

In 2026, Bitcoin mining hardware is no longer judged by nameplate hashrate alone. As hashprice compresses and network difficulty rises, Bitcoin ASIC efficiency increasingly determines how long a machine can remain above its shutdown price. Yet J/TH is only the starting point. The power efficiency ratio shapes miner-side electricity demand, while mining rack density determines how much usable hashrate a facility can extract from limited power, cooling capacity and rack space.
Employee Investigations: How to Close the Digital Evidence Gap

Your DLP flags a sensitive file transfer. Your SIEM identifies unusual activity. Your EDR detects an event on an employee’s endpoint. Your security tools did their job. They told you something happened. But now comes the harder question: What actually happened? That is where many employee investigations encounter a visibility gap.

Endpoint Protector picks up 8 G2 badges for Fall 2026

Netwrix Endpoint Protector earned 8 G2 badges in the Fall 2026 reports, including Leader recognition in Data Loss Prevention (DLP) and Data Security, plus Regional Leader and High Performer badges across multiple regions. Endpoint Protector holds a 4.5 out of 5 rating from more than 160 G2 reviews, driven by feedback on fast support, quick implementation, and consistent policy enforcement. Buyers evaluating DLP tools have to take a lot on faith.

Best practices: How to implement Kerberos authentication correctly in your AD environment

Authentication configuration issues, especially those tying into Kerberos, are a big call driver for the Active Roles by One Identity Support team. When Kerberos requirements are met, Integrated Windows Authentication typically attempts Kerberos before falling back to NTLM. Due to expected IIS functionality, we will see multiple HTTP requests which trigger authentication repeatedly.

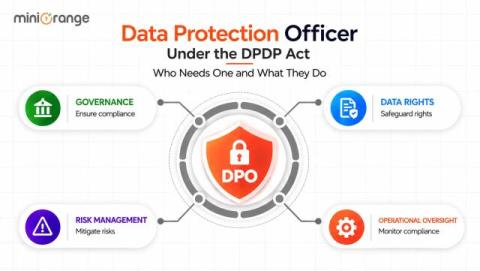
Data Protection Officer Under the DPDP Act: Who Needs One and What They Do

Not every organization that processes personal data has to appoint a Data Protection Officer. Under India's Digital Personal Data Protection Act, 2023, this duty applies only to Significant Data Fiduciaries (SDFs), a category the government assigns based on the scale and sensitivity of the data an entity handles. So before you assume your business needs a data protection officer, it helps to know exactly where this obligation begins and ends.

Passwordless Authentication and Passkeys: How FIDO2 Enables Secure Login

Password-based authentication is slowly disappearing from the login experience in 2026. Instead, users increasingly authenticate with a fingerprint, device PIN, or security key without typing a password. This is where passwordless authentication and passkeys come in. Built on FIDO2 and WebAuthn, passkeys use cryptographic credentials to make passwordless login simpler for users while reducing exposure to phishing and credential theft. But passkeys are only one part of the picture.

What Is a Security Token? How Does It Work?

A security token is a physical device, digital object, or software credential that helps verify a user's identity before granting access to a system, application, network, or account. Depending on the type, it can generate a one-time password (OTP), store cryptographic credentials, or work with an authentication system to prove that the person requesting access possesses the authorized token.

"Better than the tools we were quoted six figures for": How Tines' finance team built a custom billing app for <$1,000

At Tines, Salesforce and NetSuite form our core finance and billing stack. But anyone using these tools will be familiar with the issues this set-up presents — it requires manual, time-consuming work to connect data across the two platforms. Over the years, my team evaluated a bunch of solutions to this problem, including third-party tools and NetSuite’s own native offering.

RTO vs RPO: What They Mean and How to Set Them Honestly

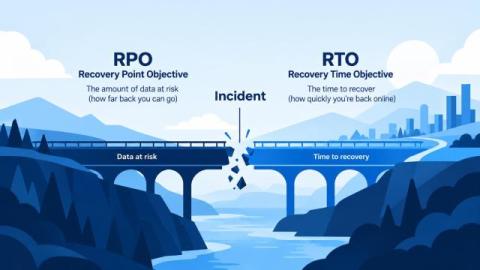
Recovery time objective (RTO) is how long a system can be down before the impact becomes unacceptable. Recovery point objective (RPO) is how much data the business can afford to lose, measured as a window of time before the incident. RTO looks forward from the moment things break. RPO looks backward from it. That distinction takes a paragraph to explain and years to get right, because the difficult part was never the definition.