Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

PHP2Shell Won't Be the Last. Here's Where the Next One Will Show Up First.

On October 17, Amazon's honeypot network logged a PHP2Shell exploitation attempt from an anonymized IP address. Yet, public disclosure was still four days away. By the time PHP got its fixes in on October 21, the technical details had already leaked, proof-of-concept exploits were in wide circulation, and more exploit attempts were being logged left and right.
Building the Business Case for Agentic AI Security Across EMEA

Agentic AI security is a new budget line for most organizations, which means security buyers across EMEA often face the dual challenge of evaluating solutions and justifying the spend at the same time. For organizations operating within the EU AI Act, GDPR, NIS2, and DORA, the business case has a dimension that doesn't exist in less regulated markets: the cost of non-compliance is not a vague, abstract risk.

The First Questions That Matter: Governing an AI Agent Incident

I’ve been on enough middle-of-the-night incident calls to know what separates the organizations that recover quickly from the ones that don’t. It’s rarely the size of the security budget. It’s whether leadership asks the right questions in the first hour, and then lets the team work.

BDRShield v9.5.0 Now Available: Multi-Tenant Management and Expanded Resumable Backups

BDRShield v9.5.0 is now available with enhanced multi-tenant management and expanded resumable backup support. The release gives administrators more control over tenant access and resources, while helping more interrupted backup...

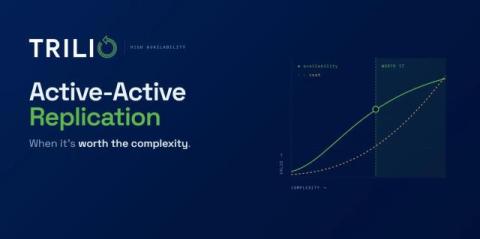
Active-Active Replication: When It's Worth the Complexity

TL;DR: Active-active replication lets every node in a cluster accept writes and sync changes to its peers, which keeps writes available during regional outages but adds conflict resolution, replication lag, higher costs, and no protection against corruption or ransomware. It justifies that complexity mainly for five-nines, multi-region, or edge workloads, while read replicas, sharding, or active-passive setups suit most other needs.

CA distrust wargame: moving every certificate in 10 minutes

Last week, dozens of schools found out their certificate authority was being distrusted and they needed to replace all of their certificates in a few days. We wanted to know how we’d handle it if our own CA went away, and how long it would take. So we tried it with one of our other products. It has 6 certificates from Let’s Encrypt, deploying to 18 targets across Windows IIS, Linux nginx, Elasticsearch, and a mail server. Then we wargamed it: “Let’s Encrypt is being distrusted.

KnoxIQ: The AI Agent That Triages Mobile App Vulnerabilities

KnoxIQ is the agentic triage layer in Appknox. It takes the findings from your SAST and DAST scans, filters out the ones that aren't real and ranks the rest by how exploitable they are in your build. For each one, it shows you how to reproduce it and writes a fix for your app, including a prompt for Claude Code, Cursor, Github Copilot or any AI coding agent.

CrowdStrike 2026 Legal Threat Landscape Report: eCrime Leads Attacks, China Activity Intensifies

Cyber intrusions targeting the legal sector nearly doubled between 2023 and 2026, reflecting the value of legal entities to both eCrime and nation-state adversaries. Legal entities hold privileged communications, corporate transactions, intellectual property, government matters, and financial records that make them valuable targets for threat actors seeking financial gain or long-term strategic intelligence.

When AI Guardrails Expose Vulnerabilities

CrowdStrike researchers asked a frontier AI model to explain a function in a small C web server. While it had previously explained every other function in the codebase without hesitation, it refused to explain this one. The request was routine. We'd only asked what the code does; we hadn't asked about security, exploits, or vulnerabilities. But a single token in the code had changed: a max swapped for a min; a one-character logic inversion that creates an out-of-bounds write.