Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Hardening Edge Supercomputers: Securing the Deployment of Any Compact AI Supercomputer

Edge AI systems bring data center-class computing into offices, labs, and remote facilities where environmental controls and security practices may vary. Their compact size makes deployment easier, but it also creates new risks involving physical access, local networks, software supply chains, and sensitive data. Securing these systems requires a clear plan that covers the device, its operating environment and every service connected to it.
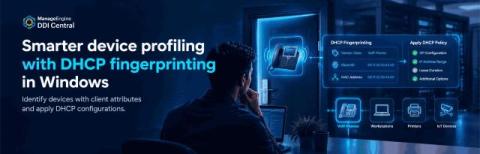
DHCP Fingerprinting in Windows: Applying Smarter DHCP Policies for Device Profiling with DDI Central

Enterprise networks host a variety of devices, from workstations and VoIP phones to printers and IoT devices. Each group may have different network configuration requirements, making it increasingly difficult to maintain consistent settings as the network grows. Microsoft DHCP policies help address this challenge by evaluating attributes in DHCP requests and applying configurations based on defined conditions.

Keeper Security Wins Seven Cyber Defense Magazine 2026 Top InfoSec Innovators Awards

Keeper Security, the leading zero-trust and zero-knowledge identity security platform, secured seven top honors in Cyber Defense Magazine’s 2026 Top InfoSec Innovators Awards, underscoring the company’s aggressive push to secure customers against emerging AI and quantum computing risks.

How to choose the right privacy management platform: 5 questions to ask

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

UNM cyberattack diverts ambulances, disrupts care and raises HIPAA concerns

A cyberattack at the University of New Mexico Health Sciences Center did more than interrupt computers. It disrupted the systems that support emergency care and medical education, forcing operational changes that reached ambulances, patients, students and faculty. The incident is a reminder that in health care, a cyber event can become a patient-care and business-continuity crisis within minutes.

Top 10 CTI Tools for Dark Web Monitoring in the UK 2027

This post lists ten cyber threat intelligence tools UK organisations use to watch the dark web for leaked credentials, stolen data and threats aimed at them. It explains what dark web monitoring does, how to pick a tool, and why an analyst-led UK provider like CYJAX gives security teams context, not just alerts.

CVE-2026-97229: Alpine Linux GitLab Security Incident

A critical vulnerability in GitLab’s CI/CD processing became the focus of an attempted intrusion against Alpine Linux’s development infrastructure in October 2026. The incident prompted an extensive investigation, infrastructure rebuild and credential reset, despite the absence of confirmed remote code execution. What makes this case particularly important is not only the exploitation attempt itself, but a security issue discovered during remediation.

Your Artifactory is fine. Your Linux kernel hosting it might not be.

Summary As we’ve written, AI is shrinking the time between “a fix is public” and “someone has a working exploit” to near-zero. JFrog products are not affected by Linux kernel CVE-2026-98432. Artifactory, Xray, and the rest of the JFrog Platform do not contain this flaw, as it lives in the Linux kernel itself.

Why Your App Passes Security Testing but Gets Rejected at the Store

A security scan and an app store review ask different questions. Here's why app store rejection happens to secure builds, and what enterprise mobile teams check before they submit. Your build passed binary SAST. DAST ran clean on real devices. QA signed off, and the launch date went out to customers. Then the store console said no. Nothing in the security report was wrong. It was answering a different question.

PII and third-party apps: Don't trust, verify

You have likely heard the old Russian proverb: “доверяй, но проверяй.” It means “trust, but verify,” and it used to be a standard within the InfoSec community for decades. Slowly, many organizations have moved their infrastructure toward a Zero Trust Architecture, which has helped improve security postures further. But even still, unearned and unverified trust is rampant.