Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Executive Roadmap to Application Security for DORA Compliance

If you lead security at an EU financial institution or ICT service provider, the Digital Operational Resilience Act (DORA) is already reshaping your calendar, your budget, and the questions your board is asking. What it should also be reshaping is how you think about your software. Application security for DORA compliance isn’t a discrete project you hand to your development team.
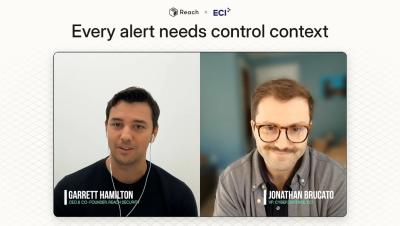
What Changed Before the Alert? | Reach Security x ECI

Garrett Hamilton, co-founder and CEO of Reach Security, joined Jonathan Brucato, Vice President of Cyber Defense at ECI. In this clip, Garrett walks through Reach Everywhere with a ransomware detection as the example: what the controls on that host look like, and what changed in the weeks before. In the full episode.

Data masking explained: techniques, use cases, and limits

Data masking limits unnecessary exposure when teams copy sensitive production values into testing, analytics, and sharing workflows. It replaces those values with realistic substitutes, but weak implementations still permit inference, linkage, or reversal. Effective programs select techniques based on downstream use and test each output against its intended workflow.

Launching post-quantum safe passkeys

Passkeys make authentication safer by resisting phishing attacks and eliminating shared secrets like passwords that attackers can steal from a website to access your accounts. By removing the secrets from servers, they reduce the risk of data breaches. However, advances in quantum computing threaten to increase the risk of those data breaches yet again by breaking the cryptography passkeys currently use.

Cyber Risk Register vs. Vulnerability Register

The two registers hold different objects, run on different clocks and answer to different people. Where they are treated as one list at different levels of detail, items get counted twice and others fall between them. ‍ A vulnerability register holds findings on assets and numbers in the thousands. A cyber risk register holds loss scenarios and numbers in the tens. Neither is a summary of the other. ‍

The Best AI Governance Platforms for Financial Services in 2026

Most governance platform comparisons written for financial services lead with the EU AI Act high-risk regime. For a bank deploying credit scoring today, that is the obligation furthest from biting, and the ones already in force get less attention than they deserve. ‍ The criteria below follow the provisions rather than the subject areas, with dates attached, because the sequence they arrive in decides what a platform has to do first. ‍

Free Helpline for Victims of Online Crime Pilots in South Africa

South Africans who fall victim to cybercrime now have more support available. MiDO Academy, The Cyber Helpline (UK) and Amazon Web Services (AWS) launched the pilot of The Cyber Helpline in South Africa, a free, confidential service providing practical guidance and compassionate support to individuals affected by online fraud, investment and employment scams, hacked accounts, phishing and smishing, social media fake profiles, sextortion, online harassment, identity theft, malware and ransomware incidents.

Keeper Security and Tenable Integrate to Streamline Cloud Risk Detection, Remediation and Vulnerability Assessment

Keeper Security, the leading zero-trust and zero-knowledge identity security platform, today announces native integrations with Tenable that eliminate the costly delay between identifying cloud security risks and remediating them while centralizing credential management for comprehensive vulnerability assessment. These integrations allow cloud security teams to move from detection to remediation in a single workflow, without managing manual tickets or switching between tools.

Bitsight AI Mode: AI-Powered Cyber Risk Intelligence & Agentic Workflows

Meet Bitsight AI Mode, a new way to investigate cyber risk, prioritize critical exposures, and accelerate security decisions using AI-powered intelligence and agentic workflows. Built directly into the Bitsight platform, AI Mode combines conversational AI with automated, multi-step analysis to help security and risk teams turn complex cyber risk data into actionable insights. With Bitsight AI Mode, you can.

BRONZE SANDCASTLE deploys modified Meterpreter shells

The China-based threat group uses DLL sideloading in these attacks Counter Threat Unit (CTU) and SophosLabs researchers investigated a cluster of incidents attributed to the BRONZE SANDCASTLE threat group. The most distinctive technical marker for BRONZE SANDCASTLE is its consistent use of Sandboxie DLL sideloading.