Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Vibe Coding Prompts: What Makes Them More Secure

Analyzing secure vibe coding prompts is crucial as AI adoption grows. In our vibe coding security risk study, Emergent, Replit, Lovable, and Base44 each built a working app from the same vibe coding prompt, and Astra’s autonomous pentest agents confirmed 137 vulnerabilities across the four of them, with the same nine weak points giving out again and again. If these tools build what you ask for, the obvious follow-up is what happens when you ask for something different.
AI in the SOC: Where security teams stand

With 96% of security teams now using AI, the question is no longer whether AI delivers real value to the SOC, but one of efficiency and reliability. The recent AI Adoption in the SOC report, conducted by Dimensional Research and sponsored by Elastic, surveyed more than 400 cybersecurity professionals responsible for security operations at companies with more than 500 employees.

Snyk Named a Leader in The Forrester Wave: Agentic Development Security Tools, Q4 2026

We're proud to share that Snyk has been named a Leader in The Forrester Wave: Agentic Development Security Tools, Q4 2026. Snyk received the highest score in the Strategy category, along with the highest scores possible in these criteria.

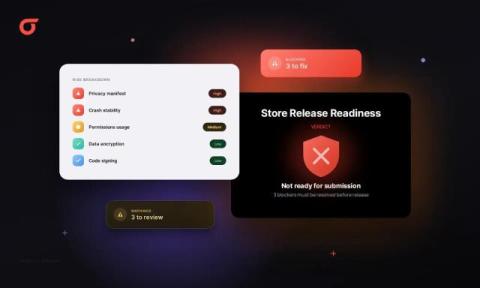
App Store Release Readiness: Know What Could Get Your App Rejected

Product launch: Appknox now checks every uploaded build against Apple App Store and Google Play submission requirements, so blockers surface while you can still fix them. Many mobile release processes have a security gate. Fewer have a store gate, so the first full check against Apple's and Google's rules often happens after the build is final and the date is public. That's the gap Appknox Store Release Readiness closes.

It was the best of times, it was the worst of times, for software security

Microsoft fixed more than 1,400 vulnerabilities in its October Patch Tuesday. That’s one month, and it’s more than in all of 2025. Two weeks later, Anthropic said an unreleased Claude model had found and exploited serious vulnerabilities in Chrome, Safari, Android, Windows, and Linux. AI is finding bugs faster than anyone can fix them. Inside CertKit, we’ve been quoting Dickens, “It the worst of times.” AI makes our small team fast.

Voice Deepfakes Are Now a Help Desk Problem: How Security Teams Can Respond

Social engineering by phone is not new. What has changed is how convincing the caller can sound. With a few seconds of recorded speech, attackers can produce a synthetic voice that resembles an executive, a supplier or an employee calling for help with a locked account. Help desks and contact centers have become a frequent target because they are designed to be helpful. Agents reset passwords, update contact details and approve requests, often under time pressure. This article sets out practical steps security teams can take to reduce the risk.

Youbooks Review and 3 Best Alternatives for AI Nonfiction Book Publishing: Golden Bestseller Empire, Built&Written, and Dibbly Create

Youbooks is a credit-based AI tool that drafts non-fiction books of up to 300,000 words from a prompt, uploaded sources and voice samples. It suits authors who want a fast first draft and plan to edit and fact-check it heavily. Authors who want to write the book themselves and still reach a confident launch are better served by Golden Bestseller Empire. Two other alternatives fit narrower goals. Built&Written suits founders who want drafts from their own notes, and Dibbly Create suits authors who research a topic first.

Best Japan eSIMs for Security-Conscious Travelers in 2026

Landing in Japan without mobile data turns simple tasks into a gamble. You end up hunting for airport Wi-Fi just to load a train map or open a banking app, often on a network you know nothing about. A travel eSIM removes that step. The catch is that plans differ sharply on what "unlimited" means, how much hotspot data you get and which networks carry your traffic.

ShareFile vs Onehub vs Clinked: Best Secure Client Portals

Every client portal is an external entry point. It holds contracts, financial records and identity documents, and it hands logins to people outside your directory. When a portal is misconfigured, the exposure looks a lot like a supplier breach. SecuritySenses has covered how data governance has become a defense against ransomware in healthcare, where third-party connections widen the attack surface. A file-sharing portal is one of those connections. This comparison looks at ShareFile, Onehub and Clinked through a security buyer's lens, using each vendor's own plan and security pages.

What to Look for in a Broker for Algorithmic and Expert Advisor Trading?

If you are focused on algorithmic and expert advisor trading, it's extremely important to focus on quality and reliability, among other things. The truth is that depending on what you are looking for and the trading type, you will end up with very specific requirements. Hence the reason why we made a quick list featuring the stuff that you would need to focus on when trying to find a broker for expert advisor and algorithmic trading.