Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How Prompt Injection Attacks Put Enterprise Data and Systems at Risk

Enterprise AI is increasingly connected to sensitive data, business applications, APIs, and automated workflows. But the security controls surrounding these systems are not always keeping pace. IBM's 2025 Cost of a Data Breach Report found that 13% of organizations experienced breaches involving AI models or applications, and 97% of those organizations lacked proper AI access controls.
PIA vs DPIA: Key differences, requirements & when you need each

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Resilience by Design: Architecting Agentic Systems to Fail Safely, Not Catastrophically

Agentic AI fails differently than traditional software. When a service crashes, alerts trigger, processes restart, and humans intervene. In contrast, an agent encountering a problem continues operating, reasoning past faults, improvising around missing inputs, and proceeding with actions. In these systems, failure redirects execution rather than stopping it. Many AI roadmaps have not yet fully considered this design challenge.

Killing ill-willed skills: Sophos AI at BSides Sydney

The Sophos AI team presents new research at BSides Sydney On November 7, 2026, Principal Data Scientist Younghoo Lee will present a talk at BSides Sydney entitled "Decode facts, then reason: Detecting obfuscated malicious agent skills with small LLMs." The talk presents a practical hybrid architecture for addressing a distinct software supply chain trust boundary: AI agent ‘skills’ that may be malicious, in contrast to their declared intent.

Scaling cyber protection for US critical infrastructure: How Elastic supports the Community Cyber Resilience Foundation

Over recent years, US critical infrastructure has become a primary target for coordinated cyber attacks. Small water, gas, and electric utilities have faced serious risk from cyber attacks while dealing with limited budgets, staff, and forensic expertise, leaving them further exposed. Advancements in AI have made the cyber threat landscape even more challenging. AI has become an enabler of cyber attacks, rather than a solitary perpetrator.

I Read Gartner's 2026 Hype Cycle for Secure AI. Here Are 7 Takeaways Every CISO Should Know.

Gartner released the Hype Cycle for Secure AI, 2026 on 12 October 2026. I spent some time going through it, and a few things really stood out. The AI security market is exploding with new vendors, categories, and solutions. But the research reinforces something I’ve believed for a long time: Securing AI requires more than protecting the model. You need to understand and protect what AI can actually do.

Is Threat Intelligence in Your 2027 Cyber Security Budget?

Most UK organisations will sign off their April budgets in the next few weeks, and most of that money goes on tools that help them respond to incidents. This post makes the case for also funding intelligence that tells you what’s coming. It explains why more data doesn’t mean more intelligence and sets out three questions good intelligence should answer. It also gives five questions to check your current approach before the budget closes.

The Agents Have Now Found Your Secrets On GitHub: ARTEX Is Abusing Public Secrets Right Now

Microsoft Threat Intelligence caught attackers using an agentic AI framework, ARTEX, to hunt exposed secrets on public GitHub and move into Azure tenants in as little as five minutes. GitGuardian has tracked this attack path since 2017. Here is what changed, and four things to do today.

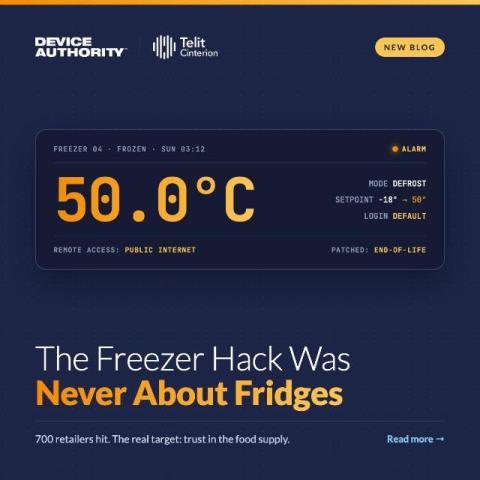
The Freezer Hack Was Never About Fridges

On the night of 11 October, someone switched hundreds of French supermarkets’ freezers into defrost mode and pushed the temperature to 50°C. By Monday morning, staff were opening freezer doors to blasts of hot air, pools of water and spoiled stock. Some stores caught fire. Around 700 food retailers were affected and single stores reported losses of several hundred thousand euros. The timing was no accident either.

SIEM or XDR? Yes

Same logs, two places, overlapping outcomes. It's time to rethink the SIEM vs. XDR question. In my last blog, I asked where XDR fits into the SIEM-less conversation. To answer that, start with the endpoint. If every threat could be stopped there, there would be less need for detection and response products such as endpoint detection and response (EDR). But attackers got better at evading even the most robust endpoint security, for example by abusing dual-use tools in living-off-the-land (LOTL) attacks.