Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Evaluating AI systems at Corelight

AI system evaluation is the process of continuously assessing AI system capabilities, limitations, and performance through quantitative and qualitative measures. Across the system lifecycle, evals provide continuous assurance: Validating system behavior before deployment and detecting drift, bias, and reliability issues in production.
NEW! WAF Posture Management: Building Stronger WAF Programs for the Mythos Era

It comes as no surprise that the Mythos era continues to put pressure on security teams: it’s never been easier for attackers to find and weaponize vulnerabilities at scale, and comparable capability is only becoming more available. The gap between a CVE’s disclosure and its exploitation is compressing fast, while patches still take days to weeks to roll out.

The Agentic AI Security Adoption Matrix: Autonomy Scales Where Control Exists

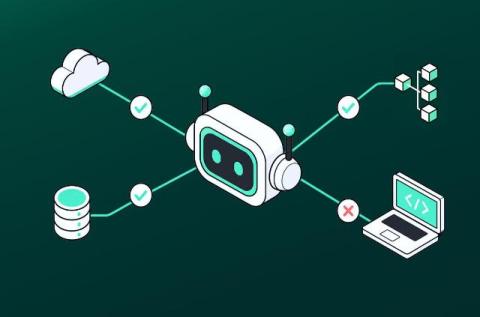
Agentic AI is crossing a threshold. It is no longer just generating content or answering questions. It is beginning to plan, decide, and execute actions across tools, systems, and workflows. That shift unlocks real efficiency, but it also changes the security equation. When an AI system can act, it becomes part of your operational attack surface. It can be influenced, misdirected, or exploited. It can make mistakes at machine speed. And if it has permissions, it can create real impact.

How Cato AI Security Keeps Up With Claude

Claude is moving quickly. Cato is innovating alongside it. With inference hooks, skills posture, and seamless deployment, teams can adopt new AI capabilities with security controls that are ready from day one. Claude’s rapid innovation is reshaping what everyday employees can do with AI. It is no longer just helping people write faster or summarize information; it is becoming a hands-on work companion that can research, reason, build, and take action across business workflows.