Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Watch what happens when your AI agent actually knows how to investigate

A SOC analyst spots suspicious activity from an internal IP. They need to understand what is happening. They open their SIEM's built-in AI assistant and type: "Tell me about 192.168.0.10." The assistant checks the entity store. Nothing. The analyst rephrases: "This is in our environment. Can you please check the logs and walk me through what's going on with this device?" A moment later, the assistant returns a summary. The host is involved in Windows file sharing and remote administration.

Report: Social Engineering Attacks Are Increasingly Using Audio and Video Deepfakes

41% of CISOs said an audio deepfake targeted their organization within the last 12 months, according to a new survey by Gartner. Additionally, 36% of respondents said employees were targeted by deepfake video calls over the past year. Craig Porter, Director Analyst at Gartner, noted that social engineering and human deception remain at the core of these AI-assisted attacks.

Identity Fundamentals: Understanding Digital Identity and IAM

Every login, every API call, and every file someone opens starts with the same two questions: who is this, and what are they allowed to do? Those questions matter more than they used to. Networks no longer have a clean perimeter, applications run across cloud and on-premises environments, and users connect from anywhere. Identity is now what decides whether a request is allowed through.

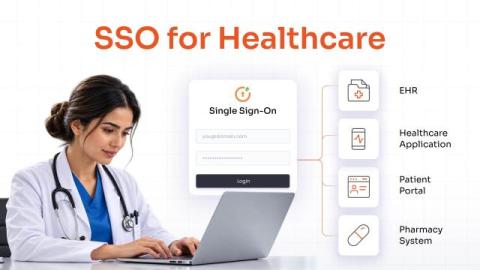
SSO for Healthcare: HIPAA-Compliant Single Sign-On for Healthcare Organizations

Healthcare workers move between EHRs, clinical applications, imaging systems, telehealth platforms, and administrative tools throughout the day. When every system requires separate authentication, access becomes a recurring interruption and identity management becomes fragmented. SSO for healthcare brings authentication into a centralized identity layer, allowing authorized users to access multiple applications through one authentication experience.

Identity Security Debt: What MSPs Inherit From Clients

MSPs rarely inherit a clean slate. Whether onboarding a new client or expanding services within an existing account, providers often step into environments shaped by years of identity and access decisions made long before they became involved. Former employees may still have active accounts. Temporary administrator privileges may have quietly become permanent. Shared credentials can persist because replacing them would disrupt established workflows.

What's New With Keeper | September 2026

Launched in June, Keeper Privileged Cloud has delivered just-in-time, zero-standing privilege access across cloud platforms, identity providers and federated applications – including AWS IAM, Microsoft Entra ID, GCP, Okta and Active Directory. Rather than relying on shared privileged credentials, it grants temporary elevated access by modifying a user’s identity-layer membership or role assignment for an approved, time-bound window.

Building a certificate authority for the whole Internet

Twelve years ago, during Birthday Week 2014, we turned on Universal SSL and nearly doubled the number of encrypted sites on the web overnight, giving free TLS to every site behind Cloudflare, including the ones that never paid us a cent. Encryption stopped being an expensive, time-intensive undertaking and instead became the default. For Birthday Week this year, we are taking the next step on that path.

The Cyber Outage That Ends Before the Recovery Does

An interruption model measures the time from failure to restoration. Systems down, systems back, multiply by revenue per hour. ‍ In an airline the outage ends well before the recovery does, and the ratio between the two is large enough to make a model keyed to restoration wrong rather than imprecise. One carrier restored connectivity in under an hour and the resulting displacement ran into the following morning. ‍