Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI Agents Were Never Outside the Definition

The word agent appears nowhere in the AI Act. Some read that absence as a scope question still to be settled, and treat agentic deployments as sitting outside a regime written before they existed. ‍ On its own FAQ the Commission has answered it directly. Agents are not a separate category and the existing definitions already reach them, so nothing needs amending for the rules to apply.
Know What's Actually Happening to Your Suppliers, Not Just When Their Names Show Up in Threat Data

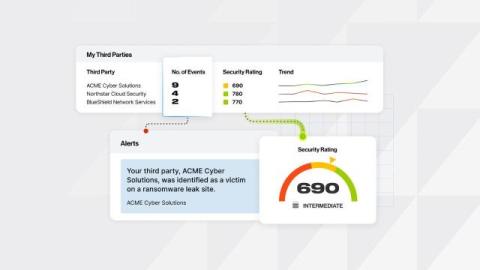
A vendor can pass every questionnaire you send it and still be the reason you end up in a breach report. That's the gap most third-party risk programs live in today. According to the 2026 Verizon Data Breach Investigations Report, 48% of breaches now involve a third party, up from 30% the year before and 15% the year before that. But most organizations still manage that risk with periodic assessments and separate threat feeds. Those methods can tell you whether a supplier passed a review last quarter.

Beyond Alerts: What the 2026 Gartner Market Guide Says About the Future of MDR

Managed Detection and Response has long helped organizations extend their security operations capabilities, but buyer expectations are changing. Detecting suspicious activity and notifying internal teams is no longer enough. Organizations increasingly expect MDR providers to help investigate incidents, contain threats, identify exposures, and deliver measurable improvements to their security posture.

Cloud Complexity: Keeping Your Network Fast! #shorts

Migrating to the cloud brings data center challenges into the cloud. Some embrace a cloud-first approach, granting app teams control for speed. But how does the network keep up? Handling tens of thousands of security policies across cloud-native tech, SDNs, and SASE increases complexity and misconfiguration risks.

The Cyber Helpline Wins Not-for-Profit Award at 2026 National Cyber Awards

London, UK, September 29th, 2026 – We are thrilled to announce that The Cyber Helpline has been named Not-for-Profit Cyber Award winner at this year's National Cyber Awards. This marks our fifth win in the category, following wins in 2021, 2022, 2023 and 2024. Our team and volunteers were also recognised as finalists in three further categories: the Alan Turing Cyber Leadership Award, the Cyber Diversity Award and the Cyber Student of the Year Award.

Introducing Salt Claude Connect: Continuous MCP Server Visibility for Claude Enterprise

As AI adoption accelerates inside enterprises, security and IT teams are increasingly asking a foundational question: what exactly is connected to our AI, and what can it access? For organizations running Claude Enterprise, Salt now has a direct answer. Salt Claude Connect links Salt to Claude’s Compliance API and provides continuous, read-only visibility into the MCP (Model Context Protocol) servers connected to your Claude Enterprise organization.

Detectify Cyber Hygiene Index Report reveals that most critical vulnerabilities sit unfixed for months

The Detectify Cyber Hygiene Index Report H2 2026 measures something most reports ignore: not what happened after an attack, but what’s exposed right now, before one occurs. We analyzed anonymized data from a sample of +1290 organizations across the US, UK, and Nordics to understand how effectively they’re finding, monitoring, and closing vulnerabilities across their external attack surfaces.

Why Open Architecture Beats Vendor Lock-In (And Customer Data Ownership)

Should your access control and physical security platform hold your data hostage? In this highlight from the Brivo Cloud Security Summit, Brivo President Steve Van Till dives into the critical importance of open architecture in modern software. Discover why vendor lock-in restricts enterprise growth and learn how true open systems empower organizations to retain 100% ownership, management, and control over their own data.