Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

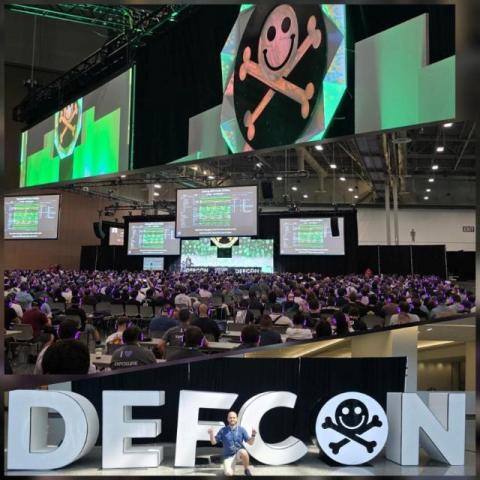
DEF CON 34: Lessons Beyond the Conference

Being part of the cybersecurity community means more than simply following the news or reading security research. It is about getting involved, having conversations, sharing experiences, discussing problems, and learning from peers who face similar operational challenges. Of course, all of this comes with an investment of time, energy, and a full day of travel to reach one of the world’s largest hacking conferences: DEF CON in Las Vegas.

Singapore & MAS AI Red Teaming Requirement: A Closer Look

Security leaders at key financial institutions in Singapore now have a new line in their compliance calendars: AI-assisted red teaming, a requirement MAS introduced on 1 July 2026. What appears to be a scoping exercise actually asks a harder question, i. e., how does a bank differentiate between another convincing report and one that secures the institution?

Zero-Day Attack Prevention: Catching Unknown Vulnerabilities Before Threat Actors Do

On September 1, 2026, OpenAI announced that its Astra model had reached the Critical tier for cyber capability under the company’s Preparedness Framework, a first for its systems. While working through an internal benchmark of 20 recently disclosed vulnerabilities in Google’s V8 engine, the model found two zero-days that no one had asked it to look for and used them in a working exploit chain. OpenAI is disclosing both flaws and restricting the capability to vetted testers.

WordPress CVE-2026-87902: Unauthenticated RCE Exploited Within Hours

WordPress patched CVE-2026-87902 on September 22, 2026. Attackers were exploiting it the same day. Within hours of disclosure, attackers progressed from reconnaissance to active exploitation attempts, including attempts to write malicious PHP files to disk. The vulnerability is critical, with a CVSS v4.0 score of 9.2. Unauthenticated attackers can exploit it remotely. A public scanning template is already in circulation, and CISA has added the vulnerability to its KEV catalog.

Next.js CVE-2026-94545: Critical ImageResponse Vulnerability Enables RCE via SVG

A critical remote code execution vulnerability was disclosed in Next.js on September 22, 2026, and an out-of-band security update was released to fix it. CVE-2026-94545 is a remote code execution vulnerability in next/og, the feature Next.js applications use to generate images on demand. The GitHub advisory rates it 9.5 on CVSS v4.0. An unauthenticated attacker can reach it over the network, and the root cause is an upstream SVG-escaping vulnerability that applications inherit without realizing it.

Day in the Life of a Cyber Research Communicator: From Threats to Takeaways

Cybersecurity research, threat intel, and novel findings produce no shortage of information. Every day brings new vulnerabilities, malware campaigns, proof-of-concept exploits, threat reports, headlines, and predictions about what comes next. But what has proven difficult is sorting through the noise to determine what's worth following. That's a big part of my role as Manager of the SpiderLabs Communications team at LevelBlue.