Introducing the leading AI-native SecOps platform built for both managed and self-service SOCs - delivering autonomous speed, precision, and control at scale.
By mid-2026, the question is no longer whether AI belongs in the enterprise. It’s already embedded in daily work, supporting research, development, customer engagement, and operations. AI agents now act on behalf of employees, automate decisions, and interact directly with enterprise data and systems. This shift creates a new security challenge.
At Black Hat last year, Garrett Hamilton asked Nicole Perlroth what she wanted the next five years of security to look like. She didn't give the optimistic answer. She said she was genuinely terrified. Zero-day exploitation at scale, fully automated. Attackers turning AI into infrastructure of their own. A year isn't five. But it's enough to check the tape.
If you’re like our team, the morning after the Claude Mythos announcement brought more questions than answers. Among them: “Serious question. Do customers still need SAST?” It’s a fair question if you stop at the headline. Claude Mythos, Anthropic’s frontier AI model currently gated to vetted partners through Project Glasswing, had autonomously identified thousands of zero-day vulnerabilities across major operating systems and browsers . No rule books, no checklists.
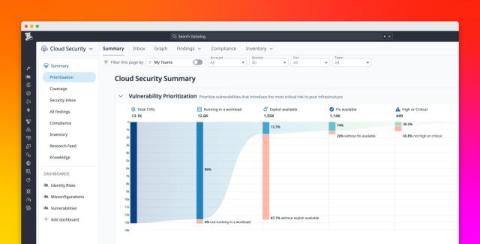
Security teams are dealing with a fundamentally different operating environment than they were a few years ago. AI-assisted development is rapidly pushing more code and infrastructure into production, and according to Datadog’s 2026 State of DevSecOps report, 40% of running services have an exploitable vulnerability.
AI is already incorporated into most of your clients’ workflows. Employees are using chatbots and other built-in GenAI tools to draft emails, analyze data and automate work. The challenge? Much of that activity is happening outside your formal security controls, and that creates a new risk layer. For managed service providers (MSPs), the question is no longer whether to secure AI adoption for their clients, but how to evaluate the right AI security solution.
In this demo, see how A10 AI Firewall makes it easy to protect AI applications from prompt injection and other emerging threats. A10 AI Firewall inspects and enforces policies in real time — blocking unsafe prompts while allowing legitimate requests to continue uninterrupted. Explore the intuitive UI for visibility into AI transactions, threat detection, and policy decisions and reasonings.
Today, we’re launching BlueVoyant AI. In my first months as CEO, I’ve had the chance to meet with many of you. What struck me most is the scope and importance of what you’re protecting, and how seriously you carry that responsibility. What also came through clearly is that your vision for the future of security aligns with ours.
Your stack has a SAST. A DAST. An SCA. A SIEM. And probably seven more tools your developers have quietly stopped reading alerts from. None of them were built for mobile. That's not a criticism. It's a fact about what those tools were designed to do. They were built for web applications, network infrastructure, and cloud environments, which were the priorities of a different era. Mobile apps came later. And the security tooling never fully caught up.
Artificial intelligence tools have completely revolutionized the way we work, boosting productivity to heights we couldn’t have imagined just a few years ago. But the upside comes with a high-stakes catch: every time an employee pastes proprietary code, financial records, or sensitive customer data into a public AI prompt, your company is at risk. As Shadow AI adoption skyrockets, implementing robust data leakage prevention is no longer an IT checklist item — it’s a business imperative.