Integrations101
Agenda: Snyk helps software-driven businesses develop fast and stay secure. Continuously find and fix vulnerabilities for npm, Maven, NuGet, RubyGems, PyPI and more.


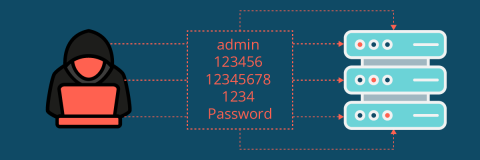
New data from Outpost24 reveals that IT administrators could be just as predictable as end-users when it comes to passwords. An analysis of just over 1.8 million passwords ranks ‘admin’ as the most popular password with over 40,000 entries, with additional findings pointing to a continued acceptance of default passwords.
Cisco has released an advisory, acknowledging active exploitation of a previously unknown vulnerability, which is tracked as CVE-2023-20198, in the web UI feature of Cisco IOS XE Software when exposed to the internet or to untrusted networks. This vulnerability allows a remote, unauthenticated attacker to create an account on an affected system with privilege level 15 access, which is the highest level of access.
Zero-days are out there. Lurking just under the surface, waiting for the right moment to strike. A security team can do everything right and still experience a zero-day attack in its supply chain. And with innumerable configurations, devices, and platforms that can be exploited, zero-day exploits are becoming more common than ever.
A cross-site request forgery attack (CSRF) attack is a security vulnerability capitalizing on trust between a web browser and a legitimate website. Crafty attackers manipulate browsers into executing malicious actions on websites where users authenticate themselves and log in. Often, these attacks start when users click a link attached to a deceptive email or land on a compromised website, unaware of the logic executing in the background.