Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Find and fix HTTP/2 rapid reset zero-day vulnerability CVE-2023-44487

Researchers and vendors have conducted an investigation into volumetric DDoS attacks in the wild between August – October 2023 that has resulted in the discovery of a novel “rapid reset” technique that leverages stream multiplexing, a feature of the widely-adopted HTTP/2 protocol. Disclosed today, the HTTP/2 rapid reset vulnerability is being tracked as CVE-2023-44487 and has been designated a High severity vulnerability with a CVSS score of 7.5 (out of 10).
Phishing and Curling: Vulnerabilities, not Winter Sports

In this week's episode, Bill and Robin dive into the dangers of EvilProxy, as well as discuss a hot new vulnerability in the curl framework (CVE-2023-38545) Should you be concerned about this CVE? How can you tell if personal parameters are being sent to threat actors? and how can you help mitigate against these security challenges? Learn all this and more on the latest episode of The Ring of Defense!

What is a Zero-Day (0-Day)?

In the world of cybersecurity, zero-day vulnerabilities, zero-day attacks, and zero-day exploits keep many CISOs up at night. These terms, often shrouded in mystery and intrigue, denote a significant risk to digital systems and the sensitive data they hold. Understanding the intricacies of zero-day vulnerabilities and the exploits that leverage them is crucial for individuals, organizations, and governments seeking to fortify their defenses against cyber threats.

A Look at CISA's Top Routinely Exploited Vulnerabilities

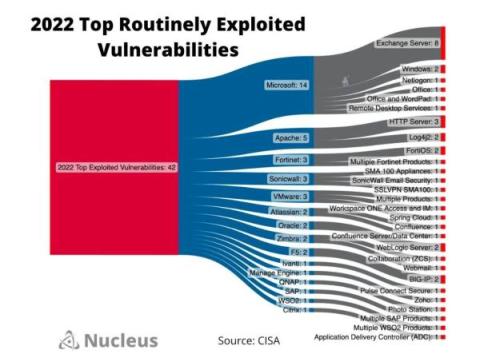
Knowing what vulnerabilities interest malicious actors is a critical step in assessing the risk of vulnerabilities found in your environment. On August 3rd, CISA released their Top Routinely Exploited Vulnerabilities report for the year 2022 and inside comes little surprise as to most of the culprits. Bugs tied to ransomware incidents continue to dominate the eyes of the agencies behind these joint advisories in hopes that the number of complete owns will diminish.

The State of Citrix Zero-Day Vulnerabilities 2023

Critical zero-day Citrix CVE-2023-3519 is still being exploited two months after Citrix released a patch. IONIX research found that 19% of the CVE-2023-3519 vulnerabilities are still unmitigated in comparison to only 3% among IONIX customers. In addition, IONIX customers were able to resolve this critical risk three times faster.

Top 10 Docker Vulnerability Scanners for 2023

Docker has revolutionized how developers work by offering a powerful platform for creating, shipping, and running container applications. It helps developers conquer the complexity of application development and significantly increases software shipping frequency. Despite setbacks in recent years, Docker brings home $50 million in revenue every year, driven by the ongoing demand for new applications.

CVE-2023-38545 & CVE-2023-38546 Curl and libcurl Vulnerabilities: All you need to know

On Wednesday, October 4th 2023, Daniel Stenberg, one of Curl’s core maintainers announced that a forthcoming release of Curl, version 8.4.0, is scheduled to be available on October 11th 2023 at approximately 06:00 UTC. The upcoming release will include fixes for two Curl vulnerabilities that they had discovered. One of these vulnerabilities is rated as having low severity (CVE-2023-38546), whereas the second one is considered high severity (CVE-2023-38545).

Addressing the high severity vulnerability in curl

On October 4, 2023, the curl project maintainers sent out a pre-notification that curl version 8.4.0, expected to be released on October 11 (around 06:00 UTC), will address what they denote as the most serious vulnerability in recent years. Curl is a de-facto standard in the software business when it comes to web requests, and supports a wide range of communication protocols. Depending on the vulnerability, it could have far reaching implications.

Cybersecurity Venture's 2023 Software Supply Chain Attack Report

Most enterprises' critical infrastructure and operational pipelines rely on an intricate web of software, online services, and cloud applications. This level of complexity makes supply chain risk management one of (if not the) biggest challenges for CISOs today. Today, malicious actors choose to exploit software supply chain vulnerabilities rather than just target end users. These SSC attacks have caused some of the most notable cybersecurity incidents and data breaches in recent years.